TEEs provide a structural way to close the institutional privacy gap by enabling bilateral confidentiality and selective disclosure on public blockchains.
As a privacy infrastructure, TEEs map cleanly onto three core institutional verticals: settlement privacy, confidential RWA onboarding, and real-time compliance, all while preserving onchain verifiability.
Oasis uses TEEs as a cross-chain privacy coprocessor, allowing existing EVM dApps to route sensitive settlement, tokenization, and KYC logic into enclaves without leaving their home chain.
Phala provides a decentralized, confidential compute layer where institutional workloads, such as order handling, credit evaluation, and fraud detection, run inside enclaves, returning only attested results for onchain settlement, onboarding, and compliance.
Primer
Trusted Execution Environments (TEEs) have become a critical building block for securing sensitive computation. By creating hardware-isolated enclaves, TEEs allow data and models to remain protected even while in use, guarding against leakage or tampering at the infrastructure level. When combined with blockchains, TEEs extend these guarantees by producing cryptographic attestations that can be verified onchain, offering both confidentiality and verifiability.
This convergence is especially relevant for institutions exploring onchain finance. As capital markets, tokenized assets, and settlement systems move onto open networks, institutions face a level of transparency that conflicts with established workflows and regulatory expectations. TEEs provide a way to preserve bilateral privacy and selective disclosure while still anchoring core workflows to a public ledger. Sensitive processes such as credit assessment, collateral checks, order handling, and compliance screening can run inside enclaves, while the chain receives only the minimal attested outputs needed to update state or complete transactions.
For a deeper introduction to TEEs and their evolution, see the previous report. If you are specifically interested in how TEEs intersect with AI, refer to this analysis.
In TradFi, nearly half of institutional trading flows through dark pools for a simple reason: information is risk. If the market can see your size, direction, or timing, it can trade against you. The specific venue mechanics differ, but the objective is consistent. Institutions rely on bilateral privacy, where only counterparties and approved intermediaries have access to the details throughout execution. Just as importantly, they rely on selective disclosure, the ability to demonstrate compliance, suitability, and best execution to regulators and auditors without broadcasting strategy to everyone else.
Public blockchains invert that norm. Transparency is the default, and it is comprehensive. Transactions, positions, liquidation thresholds, and even address clusters can be monitored in real time. Once an institution’s activity becomes attributable, observers can infer inventory, track rebalancing patterns, anticipate forced flows, and position ahead of them. The result is not just higher slippage. It is a structural deterrent to deploying size onchain because the cost of information leakage scales with capital. For many institutions, that creates an adoption ceiling: pilots are feasible, but sustained participation in lending, collateral management, and margining is harder to justify when the full lifecycle of a position is legible to the market.
Crypto has attempted to narrow the gap. Intent-based architectures, private relays, and MEV-aware routing can reduce exposure at order submission and improve execution quality in adversarial environments. But most approaches converge on the same constraint: the chain remains the system of record. Once settlement finalizes, details often reappear, either directly in calldata and state updates or indirectly via routing paths, pool interactions, balance changes, and follow-on transactions. In effect, many mitigations obscure the “before” but not the “after,” which falls short of institutional privacy requirements.
What institutions need is structural and enforceable privacy. In practice, this means maintaining bilateral confidentiality throughout execution and settlement, while preserving the ability to selectively disclose information for audit and regulatory review. Transparent ledgers make it difficult to achieve this simultaneously: maximizing privacy can weaken auditability, while maximizing auditability can reveal enough information to compromise strategy. The challenge, then, is achieving privacy with accountability: maintaining confidentiality while preserving auditability for regulators and counterparties.
TEEs as the Privacy Infrastructure
Trusted execution environments (TEEs) are hardware-based secure enclaves that enable code to run privately with verifiable execution guarantees, making them a practical approach to addressing key privacy barriers to institutional onchain adoption. The primary use cases fall into three verticals: settlement privacy, confidential RWA onboarding, and compliance.
Settlement Privacy
TEEs offer a practical foundation for private settlement infrastructure that aligns with institutional expectations. In a TEE-based workflow, trade instructions are processed within a secure enclave, where details such as asset type, amount, and counterparty remain confidential throughout execution. Only the final outcome, such as a netted transfer or settlement confirmation, is posted to the public ledger, accompanied by an attestation proving the correct logic was followed. This model preserves bilateral confidentiality while enabling verifiable execution.
This unlocks new architectures for institutional matching and netting engines. For example, multiple banks could submit encrypted orders to a TEE-hosted venue that internally matches trades based on agreed pricing logic. The TEE executes only the matched trades and submits aggregate settlement transactions to the chain, with no pre-trade or order-level data exposed. Because attestation confirms the enclave executed approved code, participants can rely on the integrity of the match without visibility into each other's flows.
TEEs are often most effective when combined with tools like zero-knowledge proofs (ZKPs), multiparty computation (MPC), or fully homomorphic encryption (FHE). A common pattern is to run an MPC-based key management system, in which key shares are distributed across multiple nodes, each operating within a TEE. This ensures that no single operator can reconstruct the private key, while the enclave enforces correct behavior and protects each share from leakage. In similar architectures, ZKPs can attest to the correctness of settlement logic, and FHE can keep selected computations encrypted end-to-end. TEEs contribute low-latency execution and the ability to run near-standard code, while ZK, MPC, and FHE strengthen trust assumptions and resilience.
Confidential RWA Onboarding
Major banks and institutions have announced tokenization initiatives and begun piloting RWA issuance, but privacy remains a key blocker to scaling these efforts. The data needed to issue and manage RWAs is inherently sensitive, including cap tables, investor registries, and other legal documentation. Institutions generally cannot expose this information on public infrastructure.
TEEs provide a practical bridge between offchain verification and onchain issuance by keeping inputs confidential while still producing verifiable outputs. In a TEE-based tokenization flow, an issuer or delegated service provider submits encrypted materials into an enclave, such as custody attestations, asset schedules, and offering terms. The enclave runs predefined checks, for example, confirming the custody statement supports the declared supply, validating eligibility constraints, and ensuring issuance logic follows the approved rules. If the checks pass, the enclave emits an attested authorization that an onchain contract can use to mint or unlock the tokenized asset, without publishing the underlying documents or raw fields.
This can significantly reduce the cost and friction associated with traditional onboarding, which is often driven by multiple intermediaries and manual verification.
Compliance
TEEs are practical for real-time compliance because they combine low-latency execution with strong data confidentiality. Unlike other privacy-preserving technologies that require heavy cryptographic processing, TEEs can handle verification logic and compliance workflows in near real time. For example, confidential AML and KYC screening can be run entirely within the enclave: user data is encrypted at rest and in transit, screened against OFAC and PEP lists inside the TEE, and produces only a pass or fail output, along with a risk score. Regulators can access a full audit trail through enclave-secured channels, while the public or counterparties see only the final compliance status.
This same framework can be extended to support dynamic transaction monitoring. Suspicious activity reports (SARs) can be triggered inside a TEE when patterns like structuring or layering are detected across encrypted transaction flows. Crucially, these alerts are shared only with designated compliance officers, preserving user privacy and avoiding false signaling to the broader market. For example, compliance checks can be executed inside a TEE at transaction time, screening encrypted activity against sanctions lists or policy rules and emitting only an approval or rejection with an auditable proof. Regulators can later review encrypted logs through authorized access, while user identities and transaction details remain private.
By enabling these types of workflows without compromising speed, TEEs offer institutions a regulatory toolset that is both responsive and privacy-aligned. Their ability to enforce policies instantly, while retaining encrypted logs for selective audit, gives compliance teams confidence that rule enforcement can scale with onchain activity without introducing operational bottlenecks.
Active Implementation
Oasis
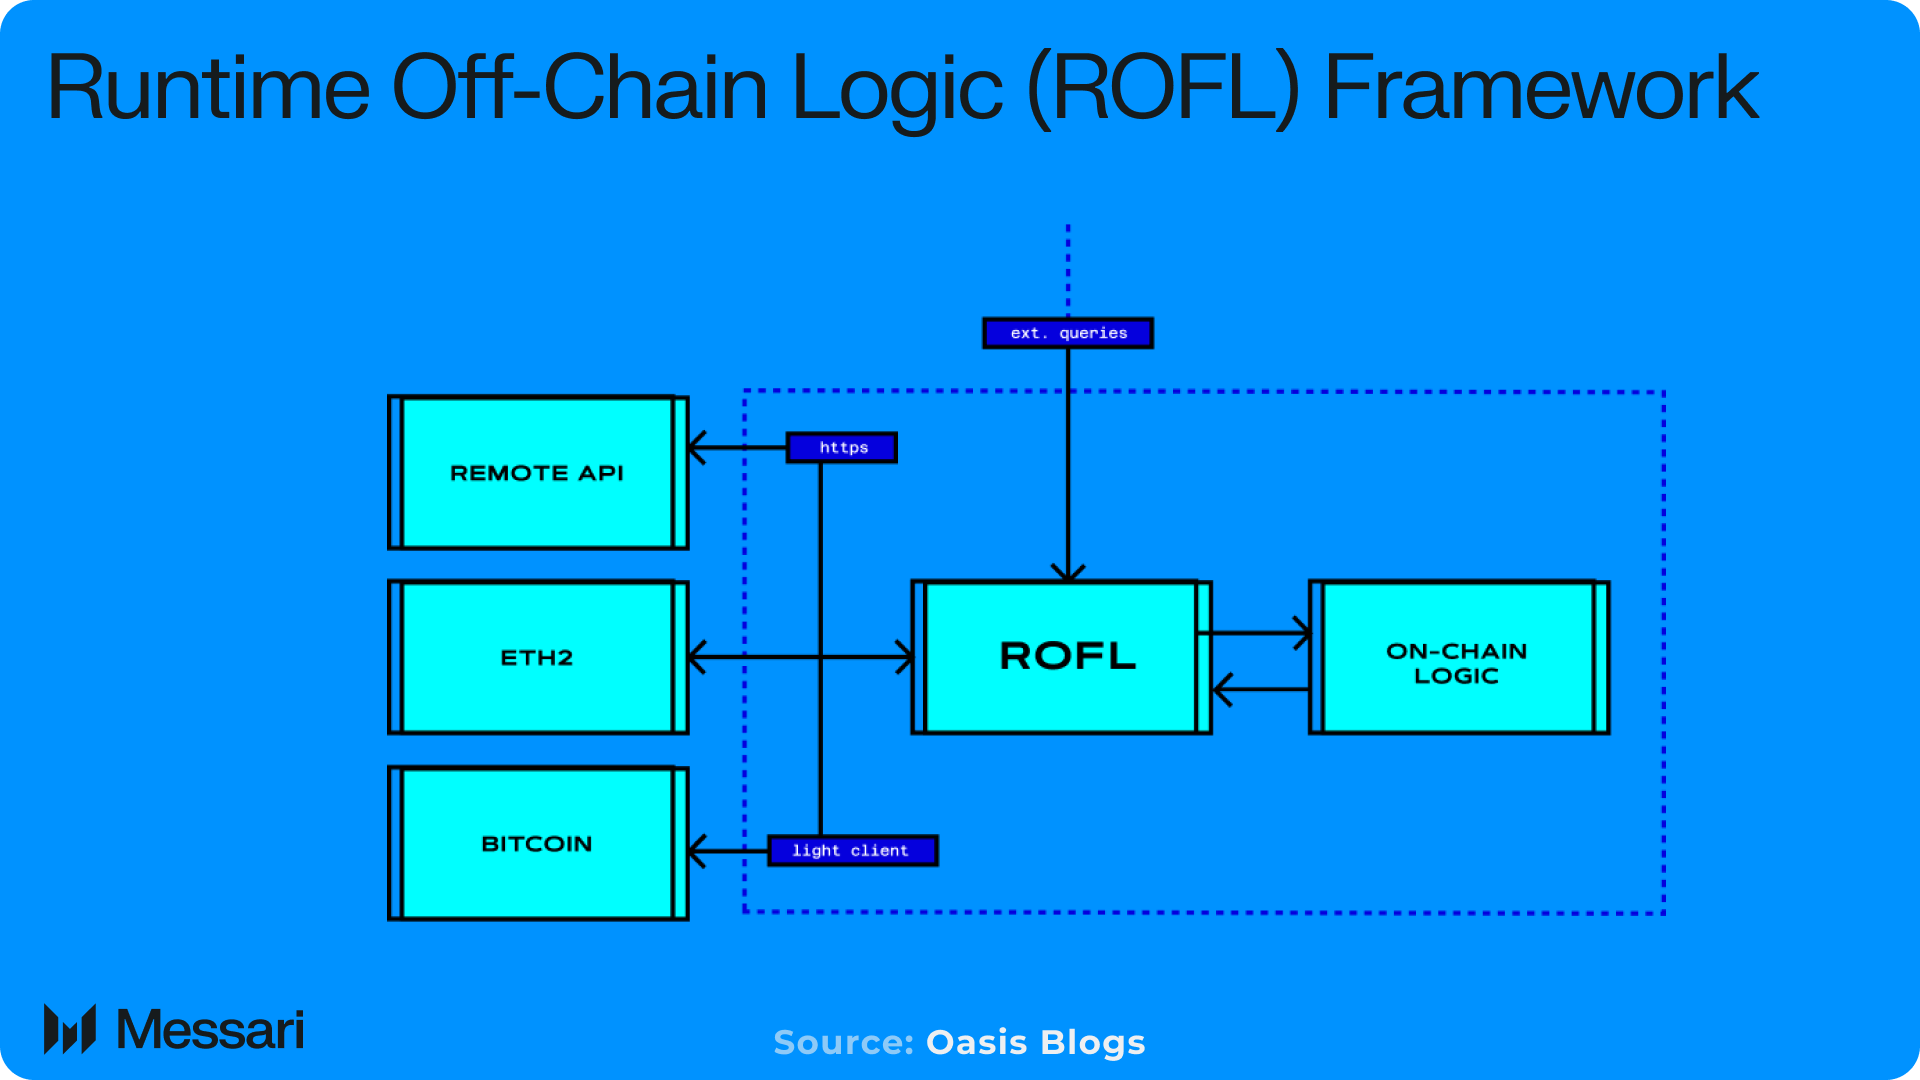
Oasis is a trustless and private execution layer that enables offchain execution with cryptographic guarantees, allowing data and application logic to remain private while producing verifiable onchain proofs. Built on TEEs, the platform combines Sapphire, a confidential EVM network, with the Runtime Offchain Logic (ROFL) framework, which supports arbitrary application execution within secure enclaves backed by continuous attestation.
This architecture provides a practical foundation for institutional use cases. Sensitive operations are executed inside encrypted enclaves, verifiable results are committed onchain, and applications remain chain-agnostic, integrating where needed without migrating assets or logic. For workflows that require both confidentiality and verifiability, Oasis enables selective routing of specific operations through confidential compute while preserving composability with public blockchain infrastructure.
An early institutional deployment is SemiLiquid’s Programmable Credit Protocol, which enables credit activation on tokenized collateral without requiring assets to leave custody. The protocol manages collateral locking, margin enforcement, and liquidation triggers using Oasis’s confidential compute stack. Its Liquefaction primitive, built on TEEs, enforces credit policies and monitors breaches while keeping counterparty information and sensitive financial data encrypted throughout the credit lifecycle.
Phala Network
Phala provides a decentralized, confidential computing layer that enables institutions to run sensitive logic within TEEs while maintaining their primary operations on existing chains or infrastructure. Its architecture separates encrypted offchain computation from onchain coordination, allowing data to remain private during processing while still producing verifiable outputs. This provides institutions with a means to enforce privacy for workloads such as order handling, credit evaluation, or data aggregation, without exposing internal models, client information, or proprietary logic.
Instead of sharing raw financial documents, underwriting data, or identity attributes, institutions can send encrypted inputs to Phala enclaves and receive attested results that downstream smart contracts can trust. For example, an issuer could verify asset eligibility or custody backing inside a TEE and return only a mint authorization to an onchain RWA contract. Similarly, a trading venue could run matching or risk checks privately in Phala while publishing only the final settlement transfers. Compliance workflows also benefit: sanctions screening, jurisdiction checks, or exposure limits can run confidentially, with the chain receiving only pass or fail signals, and regulators receiving encrypted audit logs when required.
Phala’s financial services case studies demonstrate how this approach is applied in practice. In one deployment, multiple institutions trained fraud detection models collaboratively without revealing their underlying datasets, using TEEs to aggregate encrypted updates into a shared model. In another, a trading platform processed tens of billions in daily volume by executing order flow and algorithmic logic inside enclaves, ensuring client confidentiality while still producing verifiable settlement outcomes. These examples show how Phala’s TEE layer can serve as a privacy coprocessor for institutional applications, enabling confidential computation with attested integrity across settlement, onboarding, and compliance workflows.
Closing Summary
TEE-powered infrastructure reflects a shift in how institutions can practically engage with public blockchains, introducing a programmable confidentiality layer that complements existing chains. This model preserves the performance, liquidity, and composability of open networks while enabling private execution where transparency breaks down. Across settlement, onboarding, and compliance, the pattern is consistent: sensitive logic is executed offchain within enclaves, the blockchain records only the minimum attested outputs required for correctness, and regulators retain a clear path for selective oversight.
As Oasis, Phala, and others continue deploying these systems, the broader crypto landscape is evolving from privacy as an add-on to privacy as an architectural primitive. Institutions no longer need to choose between full transparency and complete trust in centralized intermediaries; instead, they can adopt hybrid workflows where enclaves enforce confidentiality and chains enforce correctness. If successful, this model positions TEEs as a foundational component of the next generation of institutional DeFi, enabling capital markets, tokenized assets, and regulated financial products to operate onchain with the privacy and accountability they require.
This report was commissioned by Oasis Protocol and Phala Network. All content was produced independently by the author(s) and does not necessarily reflect the opinions of Messari, Inc. or the organization that requested the report. The commissioning organization may have input on the content of the report, but Messari maintains editorial control over the final report to retain data accuracy and objectivity. Author(s) may hold cryptocurrencies named in this report. This report is meant for informational purposes only. It is not meant to serve as investment advice. You should conduct your own research and consult an independent financial, tax, or legal advisor before making any investment decisions. Past performance of any asset is not indicative of future results. Please see our Terms of Service for more information.
No part of this report may be (a) copied, photocopied, duplicated in any form by any means or (b) redistributed without the prior written consent of Messari®.
Alice is a Research Analyst on the Protocol Services team. She previously worked as a Research Analyst at The Block and was an Investment Intern at Variant Fund. Alice graduated from Northwestern University, where she studied Economics.
Alice is a Research Analyst on the Protocol Services team. She previously worked as a Research Analyst at The Block and was an Investment Intern at Variant Fund. Alice graduated from Northwestern University, where she studied Economics.