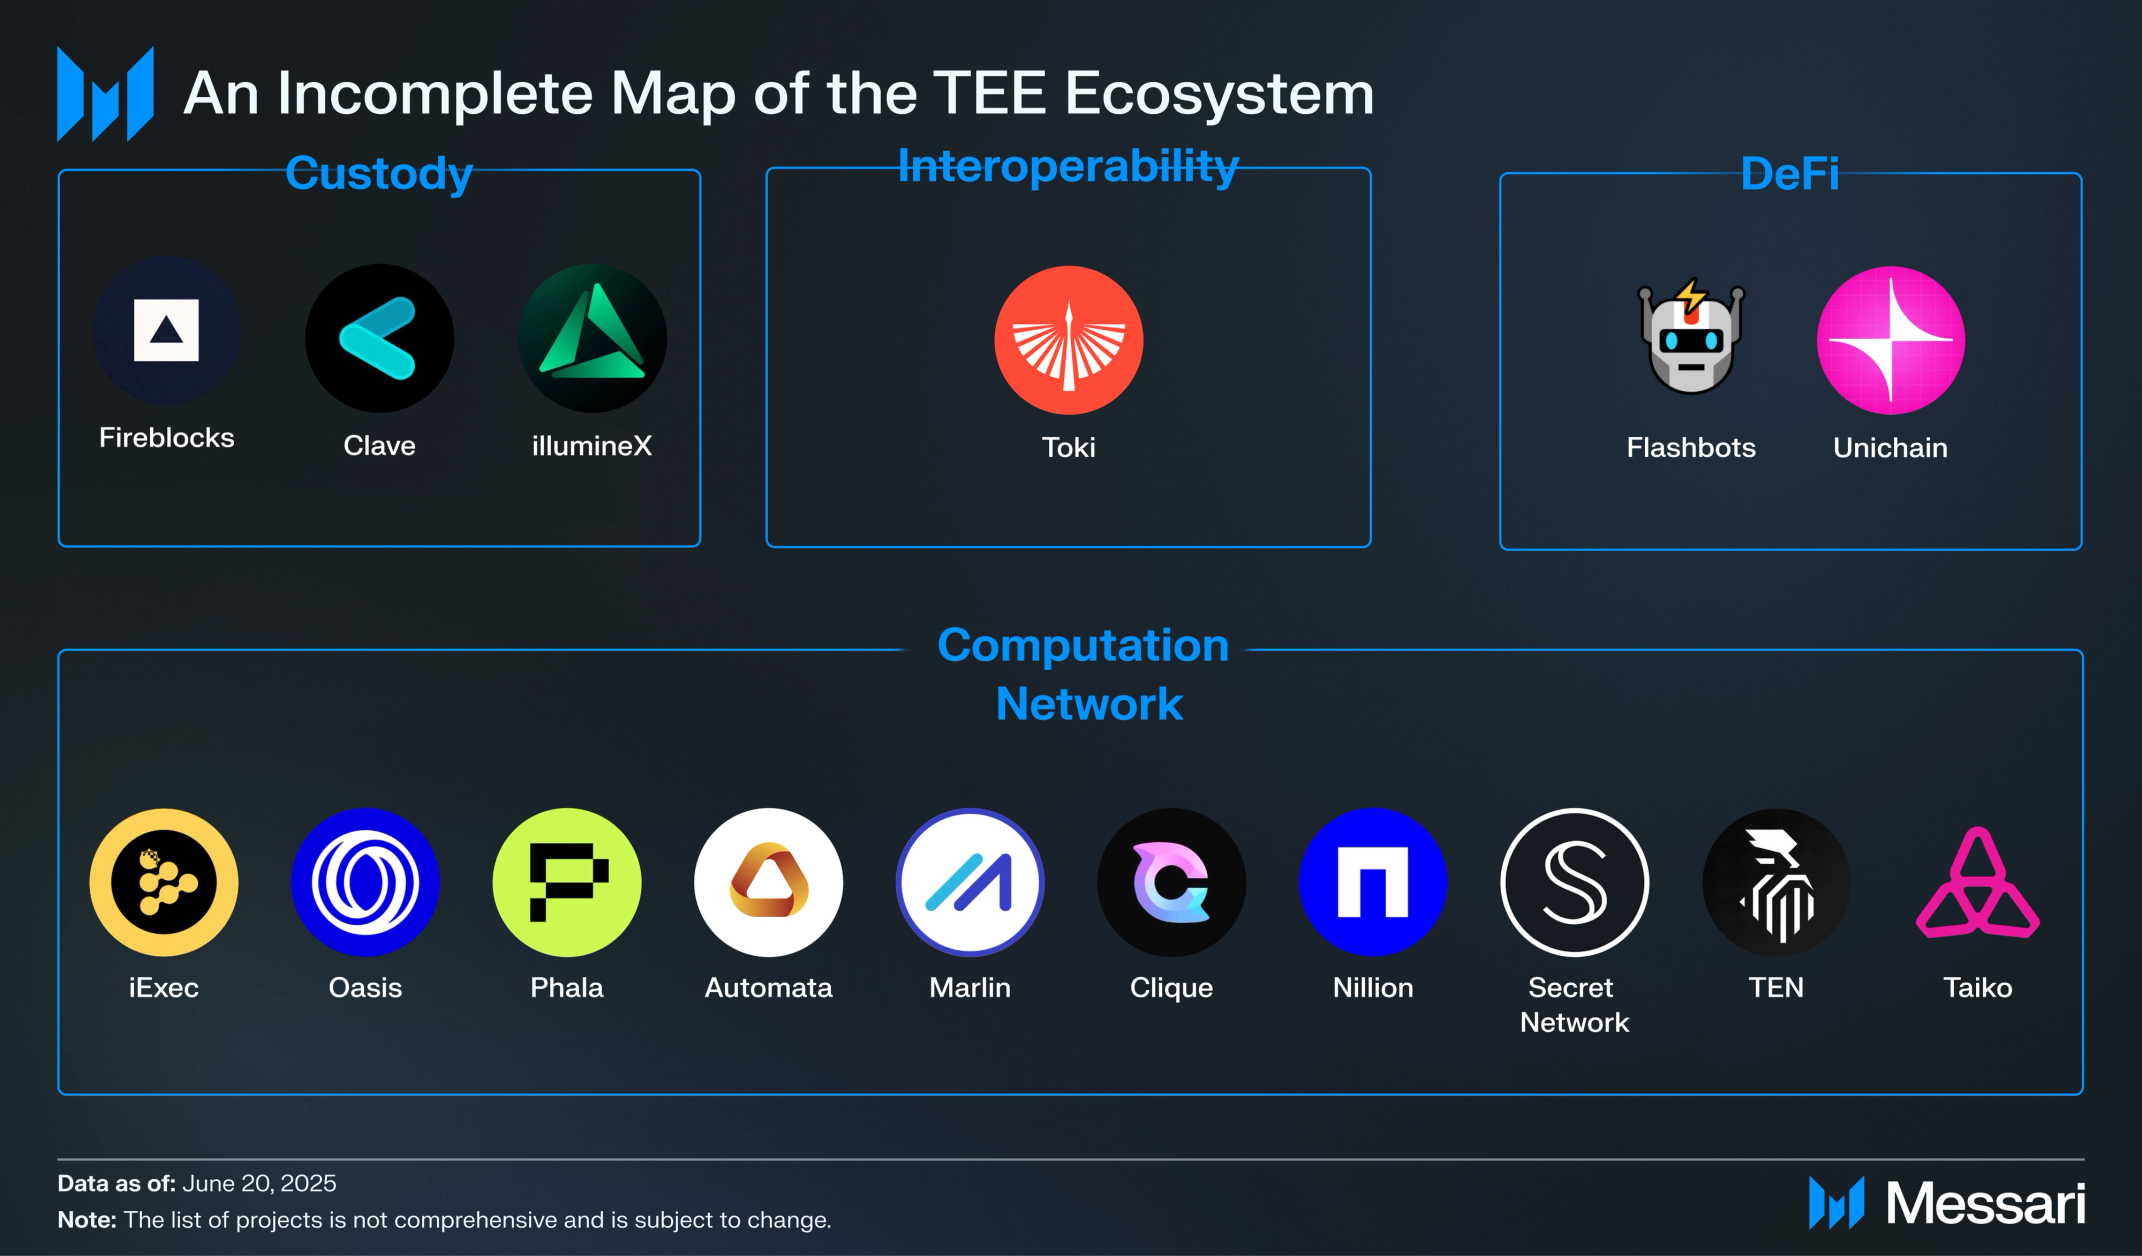
TEEs are increasingly integrated into blockchain protocols, with projects like iExec, Oasis, and Phala Network adopting TEE-powered infrastructure to enable confidential computation and verifiable privacy at scale.
Unichain implements TEE-based block building, introducing priority-based transaction ordering, MEV resistance, and verifiable public attestations for block construction.
Custody solutions such as Clave and Fireblocks are leveraging TEEs to protect private keys and transaction signing with hardware-enforced isolation, reducing risks from both external and insider threats across digital asset management.
Primer
Trusted Execution Environments (TEEs) have emerged as a foundational security technology, creating isolated hardware spaces where sensitive computations and data can be securely processed. Unlike traditional cryptography that relies on mathematical complexity, TEEs use hardware isolation to provide a powerful layer of protection, making them especially relevant as digital systems become more complex and interconnected.
Within the blockchain ecosystem, TEEs are rapidly gaining traction as a solution to long-standing challenges in privacy, scalability, and interoperability. They allow confidential data to be processed offchain or in parallel with blockchain networks, enabling use cases ranging from private DeFi transactions to secure cross-chain bridges and AI-driven applications, all while maintaining cryptographic proofs of correctness.
This report examines how TEEs are being adopted across computation networks, custody solutions, interoperability protocols, and DeFi, and explores the new possibilities they unlock for developers, end users, and the future architecture of decentralized systems.
A Trusted Execution Environment (TEE) is a hardware-based security technology that creates a secure, isolated area within a computer processor where sensitive code and data can be processed safely. The key distinction of TEE vs. other cryptographic techniques is that TEEs leverage hardware isolation rather than mathematical complexity. For example, zero-knowledge proofs (ZKPs) and multi-party computation (MPC) are software-based approaches that rely on mathematical complexity to protect data. ZKPs enable one party to prove knowledge of a value without revealing it, while MPC allows multiple parties to jointly compute a function without exposing their inputs. For more information on the difference between TEEs vs. other cryptographic techniques, read this report.
The choice between TEEs and other privacy-preserving technologies depends heavily on specific requirements. TEEs excel in scenarios demanding high-performance confidential computing, such as private AI model training or real-time secure data processing. ZKPs shine when mathematical verifiability is paramount. Under certain scenarios, these technologies complement each other: TEEs can provide secure proof generation environments for ZKPs, combining hardware isolation with cryptographic guarantees to create robust privacy solutions.
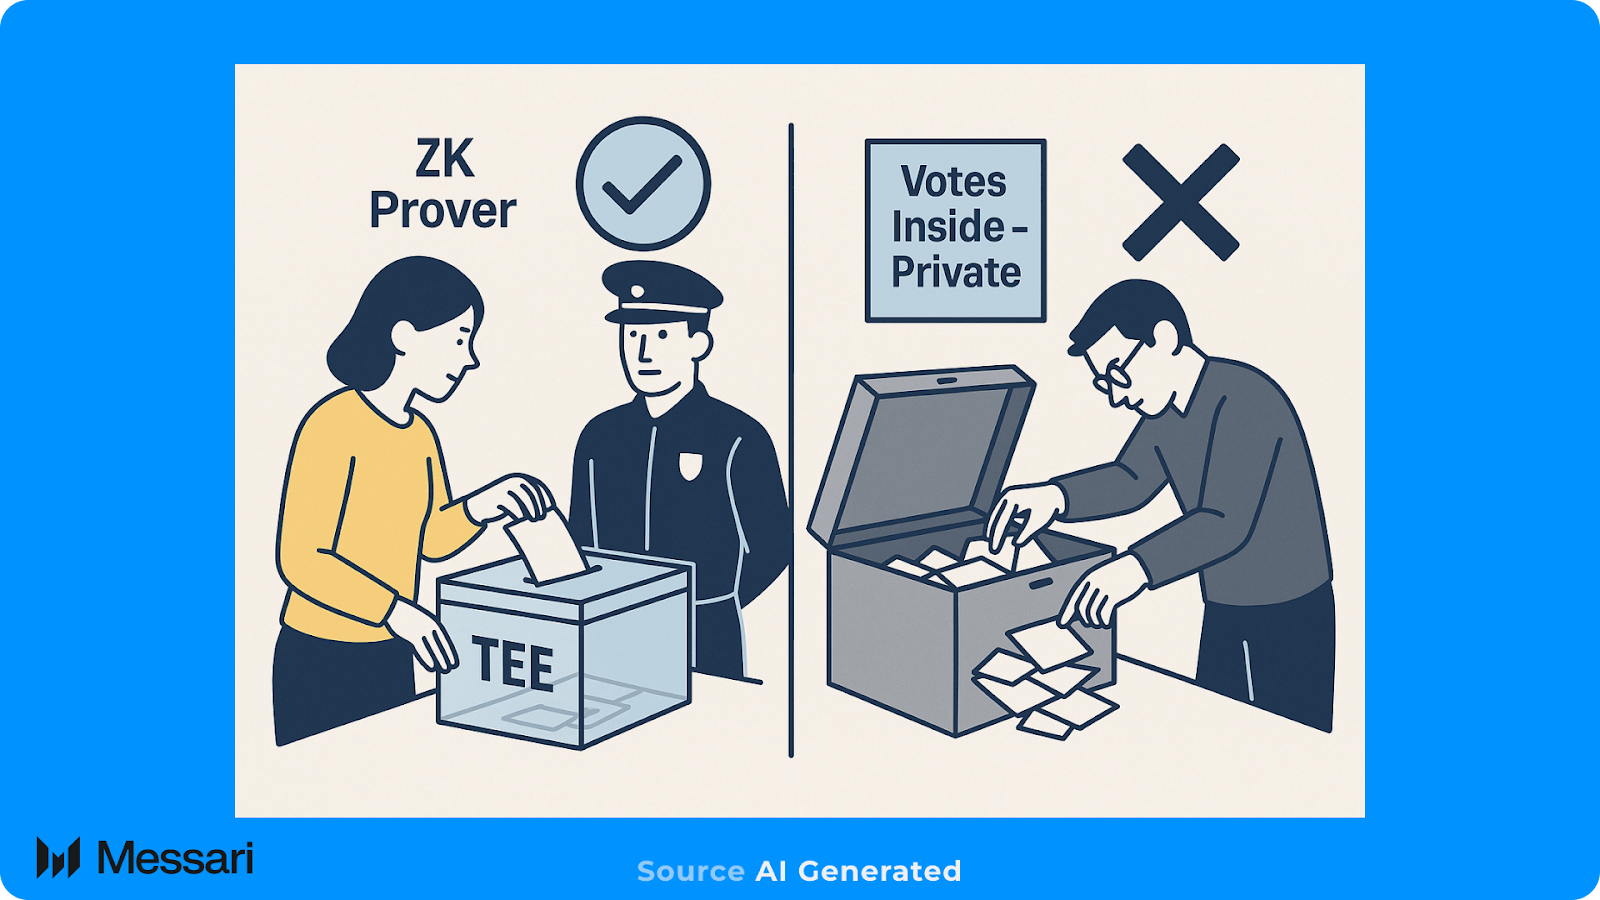
This relationship is similar to a sealed ballot box used in elections. Zero-knowledge proofs are like voters submitting their choices in secret; the box allows each person to prove they participated without revealing their vote. However, if the ballot box were left open or unguarded, someone could tamper with the contents, undermining trust in the outcome. A TEE functions as a securely locked and monitored ballot box, ensuring that the process of casting and counting votes is protected from interference. In this way, TEEs safeguard the integrity of zero-knowledge proof generation, so that the result can be trusted even though the sensitive details remain confidential.
The Evolution of TEEs
According to an a16z report written by Aaditya Shidham, TEEs have been in use since the 1990s, originally providing secure areas in hardware for applications like digital rights management, content protection, and secure payments. For example, mobile phones used TEEs to store sensitive information such as biometric data, PINs, and cryptographic keys, protecting from malware and unauthorized access.
The technology advanced further with the introduction of Intel’s Software Guard Extensions (SGX) and AMD’s Secure Encrypted Virtualization (SEV). These innovations brought TEE security to cloud computing and server environments, enabling new use cases such as confidential cloud computing, secure key management, and privacy-preserving data analysis.
Today, TEEs are foundational to the infrastructure of major technology companies. Microsoft, for example, has built extensive confidential computing services into its Azure cloud platform, allowing businesses to process sensitive data securely. Most recently, NVIDIA has introduced confidential computing capabilities on its Hopper and Blackwell GPUs, enabling secure processing of AI models and data.
TEE Adoption in Crypto
Why Do TEEs Matter to Blockchain?
A core limitation of traditional blockchain systems is their inability to process sensitive data privately while preserving the benefits of decentralized execution. Blockchains are designed for transparency: all data and smart contract states are typically visible to every network participant, which is essential for trustless verification and consensus. However, this public-by-default architecture makes blockchains unsuitable for applications where confidentiality is critical, such as private financial transactions, healthcare records, or proprietary business logic.
TEEs offer a compelling solution to these challenges. By introducing hardware-based secure enclaves, TEEs allow sensitive computations and data to be processed in isolation from the rest of the system. This means that even node operators or other infrastructure providers cannot access the underlying information, addressing privacy concerns while still enabling decentralized verification. TEEs can process confidential data offchain or in parallel with the blockchain, and only the necessary results or cryptographic attestations are posted onchain. This approach preserves privacy without sacrificing auditability, transparency, or decentralization.
Beyond privacy, TEEs also help address scalability and interoperability challenges in blockchain ecosystems. They enable complex or resource-intensive computations to be performed offchain within a secure enclave, reducing the computational burden on the blockchain itself. Additionally, TEEs can act as secure intermediaries for cross-chain operations, safeguarding the movement of assets or data between different blockchains and supporting more robust interoperability.
Adoption of TEEs in Blockchain
Usage in Computation Network
Most blockchain projects leveraging TEEs today are computation networks. These projects offer decentralized, confidential computing infrastructure that allows users to process data securely offchain, while still maintaining cryptographic proofs of correctness. Each project has its own niche in terms of product services.
For example, iExec positions itself as the trust layer for DePIN and AI by providing confidential computing, developer SDKs, and interoperability tools. iExec launched the iApp Generator, a tool that simplifies the creation of TEE-based confidential applications. To demonstrate its capabilities, iExec released user-facing apps such as the Image Description Matcher, which privately verifies if a description matches an image without revealing either party’s data, and Web3Mail, a privacy-preserving messaging tool that allows users to send emails to wallet addresses without exposing personal information.
Oasis enables confidential, verifiable computation for next-gen applications through privacy-first infrastructure, confidential smart contracts, and multi-chain developer tooling. Key products include Sapphire, the first and only confidential EVM in production, and Runtime Offchain Logic (ROFL), a framework that allows offchain apps to leverage onchain trust. ROFL streamlines TEE development with support for complex AI workloads and real-world integrations while maintaining blockchain verifiability. A notable example is WT3, a trustless AI trading agent built on the Oasis TEE stack.
Phala Network delivers a trustless cloud platform, Phala Cloud, that allows developers to deploy applications into secure TEEs for confidential AI and data processing. The network combines TEEs with other cryptographic technologies such as MPC and ZKPs to enable verifiable and privacy-preserving computation at scale. Phala also published the first GPU-TEE benchmark by running Large Language Models (LLMs) on NVIDIA GPUs, establishing a reference point for privacy and performance in decentralized AI. The results validate the scalability of TEE mode for large-scale LLM Inference tasks.
Usage in Custody and Key Management
Custody solutions are increasingly using TEEs to protect private keys and sensitive operations with hardware-level security. Clave, for example, is integrating Nvidia’s TEEs on GPUs to offer privacy-first AI services and secure asset management, enabling features like passkey authentication and biometric protection with end-to-end confidentiality. Fireblocks takes a multi-layered approach, combining MPC with confidential computing enclaves in the cloud to keep key management and transaction signing isolated and secure, protecting assets from both external attacks and insider risks. Oasis Sapphire enables trustless key management by storing private keys directly in confidential smart contracts, where they remain encrypted and can only be accessed within secure enclaves, eliminating the need to trust developers, operators, or third parties with sensitive credentials.
Usage in Interoperability
TEEs are also critical for securing cross-chain bridges and interoperability protocols. By running bridge logic and key management inside a secure enclave, TEEs protect against manipulation and unauthorized access, which have historically plagued cross-chain solutions. Projects like Toki use TEEs to unify cross‑chain transaction standards and enable confidential data transfer between blockchains. This setup supports confidential key exchange and fine-grained access control, greatly reducing risks of data leakage or tampering during transmission.
Usage in DeFi
TEEs are rapidly being adopted in DeFi to improve fairness, privacy, and transparency in transaction processing. Unichain is the first Layer 2 (L2) to build blocks inside a TEE, using Rollup Boost co-developed by Uniswap Labs and Flashbots. This setup enforces priority-based transaction ordering and processes transactions in a private, encrypted mempool, reducing extractive MEV and enabling public attestations for verifiable block building. With features such as revert protection, where users avoid gas fees on failed transactions, TEE-based designs are setting new standards for predictability, decentralization, and user experience in DeFi.
The Path Forward
The next phase for TEEs in crypto will be defined by their move from niche infrastructure to critical backbone for privacy, compliance, and AI-driven applications. As GPU-based TEEs, such as those from NVIDIA, become mainstream, confidential computing will unlock secure, high-throughput AI inference, private agent economies, and onchain verification of complex models. This will significantly enhance blockchain capabilities for enabling AI-integrated applications with built-in privacy at scale.
However, this progress also brings in new trust models and transparency standards. As TEEs play a larger role in cross-chain bridges, block building, and oracle networks, the crypto ecosystem will need to address concerns around hardware supply chains, remote attestation, and the risk of centralization by TEE manufacturers. Ultimately, TEEs are poised to evolve from a “nice-to-have” for privacy into an essential, composable primitive for compliant, scalable, and AI-integrated Web3 systems.
As the landscape evolves, teams are shaping the future of TEEs. Here’s what leaders from iExec, Oasis, and Phala have to say:
“The combination of blockchain and TEE will only get stronger and more valuable as TEE technologies become more diverse and pervasive. At the same time, end-users are challenging service providers and demanding that they do more to protect the private data that they hold. The next few years will likely see massive adoption, supported by emerging mainstream confidential applications.” - iExec (Anthony Simonet-Boulogne)
“Having worked with TEEs for many years, we've witnessed their rise across the broader crypto space. By ensuring privacy and verifiability, they enable onchain confidentiality, extend blockchain runtimes, and address critical trust issues around AI. As adoption continues to grow, TEEs are positioned to unlock new use cases for sensitive data and serve as a primary catalyst for trustless agents.” - Oasis (Matej Janež)
“In a future shaped by Safe AGI, trust is the foundation. By combining TEEs with blockchain, we empower builders to create AI systems that people can truly trust—secure, transparent, and privacy-preserving. This synergy is key to unlocking AI that respects user sovereignty and fosters widespread adoption.” -Phala (Marvin Tong)
Closing Summary
TEEs are moving from background infrastructure to a strategic lever for reshaping what blockchains can securely support. As they become more accessible and integrated into core protocols, TEEs enable decentralized systems to process sensitive data, coordinate across chains, and power AI applications with strong guarantees on privacy and correctness. The real impact will be felt as projects move beyond privacy for its own sake, using TEEs to unlock fundamentally new forms of value transfer and coordination that were previously impossible on open networks. The participants who succeed will be those who can deliver these capabilities seamlessly to both developers and end users, setting a new bar for onchain experiences.
This report was commissioned by iExec RLC, Oasis Protocol, and Phala Network. All content was produced independently by the author(s) and does not necessarily reflect the opinions of Messari, Inc. or the organization that requested the report. The commissioning organization may have input on the content of the report, but Messari maintains editorial control over the final report to retain data accuracy and objectivity. Author(s) may hold cryptocurrencies named in this report. This report is meant for informational purposes only. It is not meant to serve as investment advice. You should conduct your own research and consult an independent financial, tax, or legal advisor before making any investment decisions. Past performance of any asset is not indicative of future results. Please see our Terms of Service for more information.
No part of this report may be (a) copied, photocopied, duplicated in any form by any means or (b) redistributed without the prior written consent of Messari®.
Alice is a Research Analyst on the Protocol Services team. She previously worked as a Research Analyst at The Block and was an Investment Intern at Variant Fund. Alice graduated from Northwestern University, where she studied Economics.
Alice is a Research Analyst on the Protocol Services team. She previously worked as a Research Analyst at The Block and was an Investment Intern at Variant Fund. Alice graduated from Northwestern University, where she studied Economics.