Arcium is emerging as a foundational encrypted compute layer built around MPC, enabling verifiable yet fully private computation for Web3 applications spanning DeFi, AI/ML, and institutional data sharing.
Mainnet Alpha introduces a production-ready encrypted compute environment with curated node participation, developer SDKs, and early partner integrations.
Arcium’s Testnet had over 3,000 distributed nodes, 30+ deployed applications, and 300+ hackathon submissions validating developer interest in encrypted compute and demonstrating Arcium’s capacity to coordinate MPC workloads at scale.
Arcium is also developing the Confidential SPL token standard (C-SPL), which transforms privacy on Solana from a transaction-level feature into a programmable capability, allowing token logic to be executed confidentially through Arcium.
Primer
Arcium is a decentralized, encrypted compute protocol designed to enable secure multiparty computations (MPC) and private processing for blockchain applications. The protocol allows developers to run complex logic or data processing privately, then send verified results back onchain without revealing sensitive inputs.
Today, most blockchains lack native privacy and struggle to support computationally intensive workloads without compromising decentralization or transparency. Zero-knowledge (ZK) systems can provide verifiability but often struggle with a lack of expressivity and performance constraints, while trusted hardware solutions sacrifice trust minimization. Arcium’s model offers an alternative: a network of independent compute nodes that jointly execute encrypted workloads, ensuring no single party can see the underlying data while still producing usable outputs.
Solana was architected to maximize throughput, composability, and transparency, with all transactions, account states, and program logic publicly visible by default. This design choice enabled fast execution and onchain interoperability but left privacy as an application-layer concern rather than a native protocol primitive. As a result, early Solana development prioritized performance and openness over encryption.
Eventually, the Solana Foundation introduced targeted privacy primitives to address specific limitations. The Token-2022 standard, introduced in Q1 2024, enabled support for confidential transfers, allowing token balances and transfer amounts to be hidden while maintaining compliance and auditability. Other approaches, including shielded balances and privacy-focused applications, further demonstrated that privacy could coexist with Solana’s performance model. However, these solutions were largely transaction-scoped, offering privacy for balances or transfers rather than for arbitrary logic or complex computation.
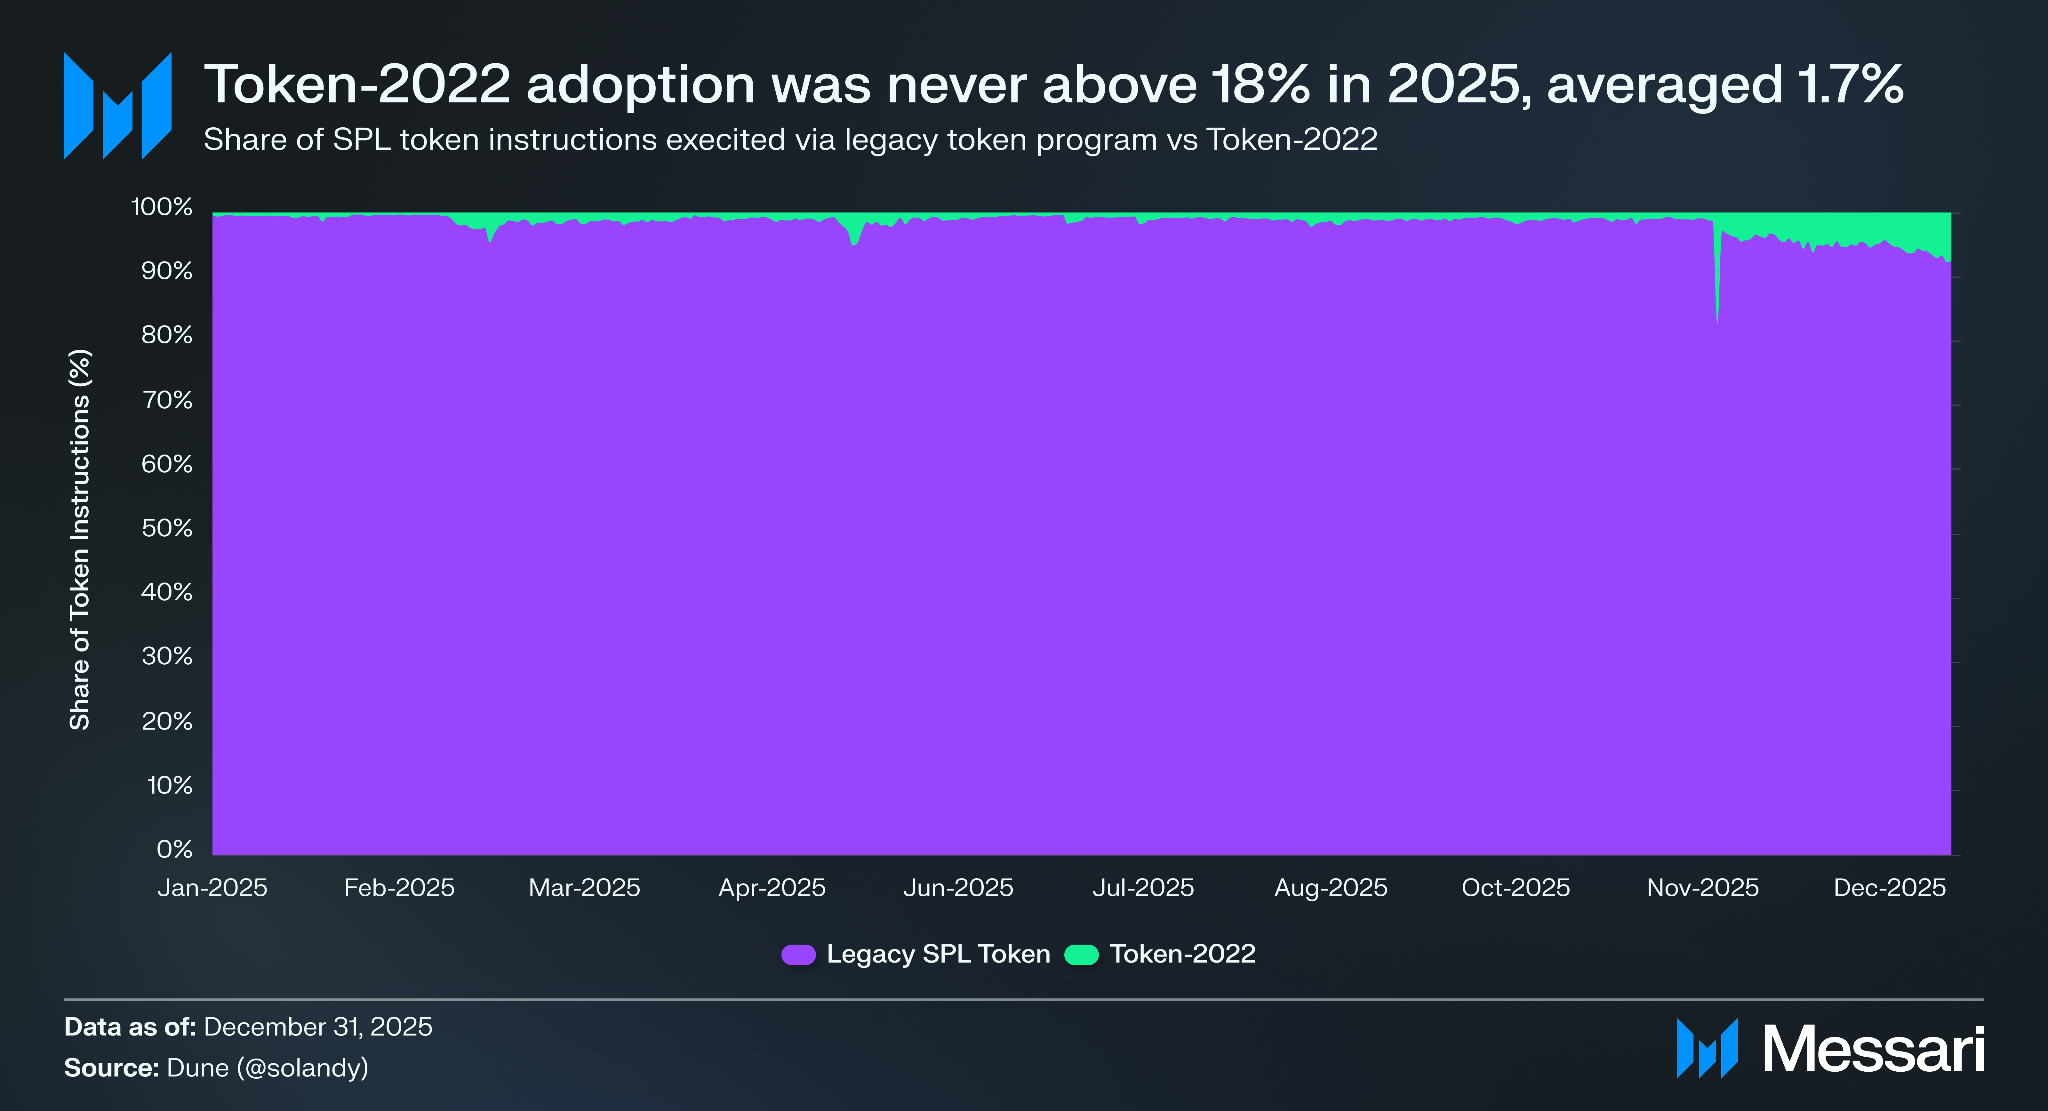
In 2025, adoption of the Token-2022 standard was minimal to none at the instruction execution level. The Token-2022 standard lacked the ability to use confidential tokens in DeFi, and users had to pre-create accounts to be able to receive confidential tokens, resulting in a difficult developer experience. What remained missing was a general-purpose, confidential compute layer capable of executing custom logic on encrypted data while preserving verifiability and minimizing trust. Advanced use cases, such as private DeFi strategies, confidential order flow, secure auctions, or collaborative data analytics, require more than private transfers; they require private computation, which is what Arcium’s Confidential SPL (C-SPL) Standard solves. C-SPL works with any onchain program and has a simple developer experience.
Although adoption with Token-2022 was small, the market was signaling that privacy remained an important piece of the onchain puzzle. Zcash and Monero, two popular privacy coins, saw their market caps grow by over 900% and 200%, respectively, in 2025. However, Zcash and Monero only give privacy on their respective blockchains and lack support for smart contracts, so the privacy is only extended to the volatile asset and transfers. Arcium emerges to fill this gap by extending Solana (eventually multiple blockchains) with a trustless, verifiable offchain compute network, enabling privacy as a programmable capability rather than a narrow feature, enabling Encrypted Capital Markets
Arcium Overview & Team History
Protocol Overview
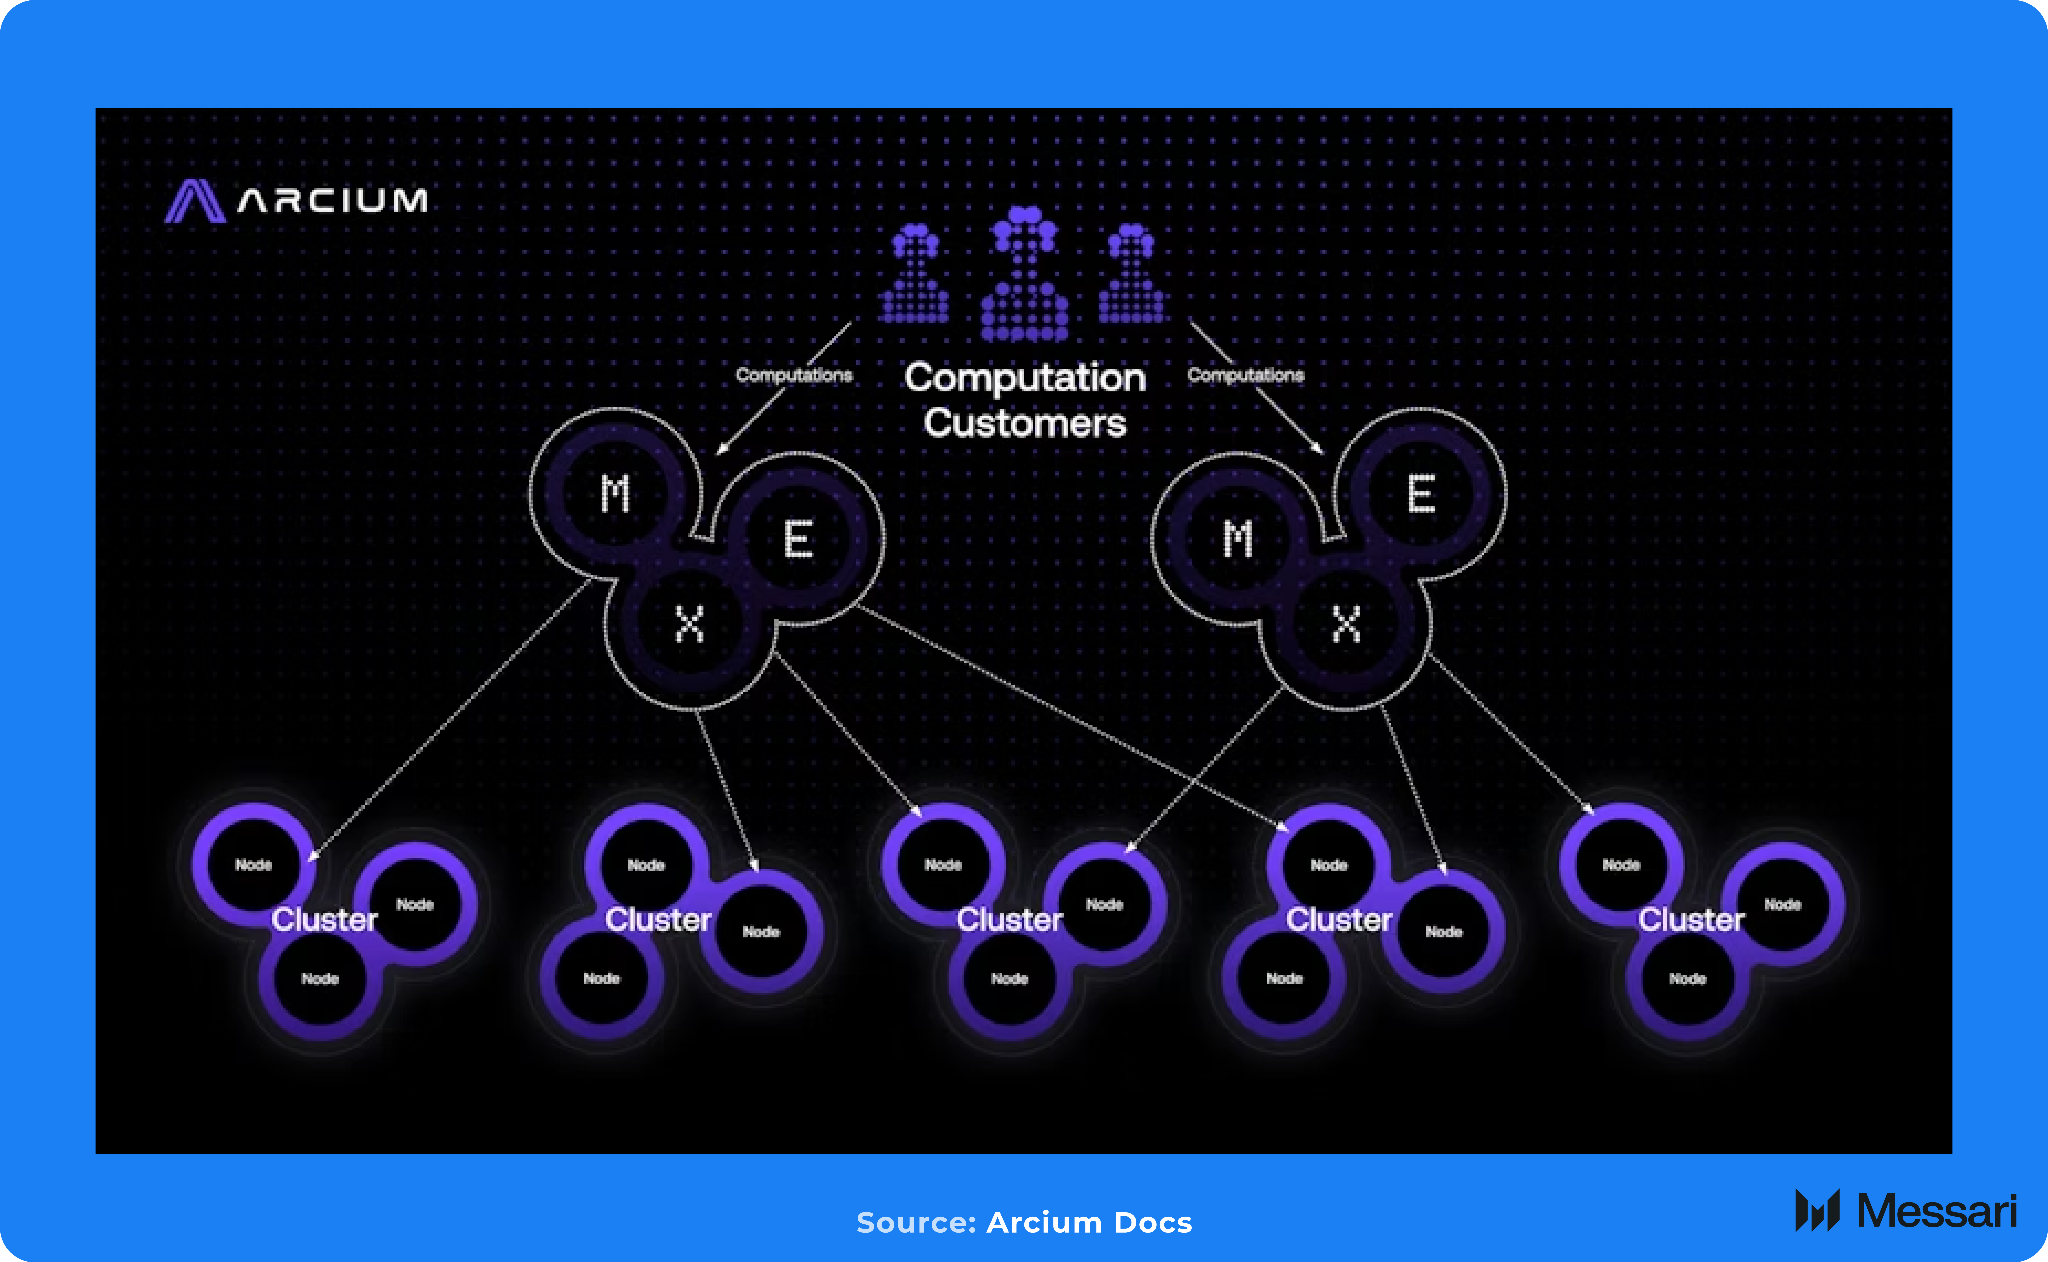
Arcium is a decentralized network of nodes that jointly process encrypted computations. Developers write “formulas,” or computation tasks, which are broken into shares and distributed across multiple compute operators. No single operator can reconstruct the original data, ensuring encryption throughout execution. The network supports a range of use cases, from private DeFi logic to machine learning inference and data-sharing agreements between institutions. Arcium functions like an encryption coprocessor for Solana, similar to how GPUs offload heavy computation from CPUs; Arcium offloads sensitive computation from Solana.
Arx Nodes and Clusters: The network is composed of decentralized Arx Nodes, each acting as a single processor. These nodes cluster together to execute computations on encrypted data. To ensure network integrity, nodes must stake collateral, and any misbehavior results in penalties, including the slashing of staked tokens.
arxOS: This is defined as the distributed execution engine, effectively functioning as a distributed, encrypted operating system that manages the activities of the Arx Nodes.
MXEs (Multi-Party eXecution Environments): MXEs are the backbone of the computation layer. They function as configurable virtual machines that enable self-contained, Byzantine fault-tolerant execution of MPC protocols. MXEs can be thought of as locked conference rooms where multiple independent parties jointly review sensitive documents. No single participant ever sees the full document, but the group can still reach a verifiable conclusion.
Arcis Framework: Arcis is the developer framework designed to minimize the learning curve for integrating encrypted computing. It extends the familiar Anchor tooling used by Solana developers, allowing them to leverage Rust and add privacy by simply marking desired functions as encrypted. This focus on developer experience underscores the commitment to seamless integration into existing Web3 workflows.
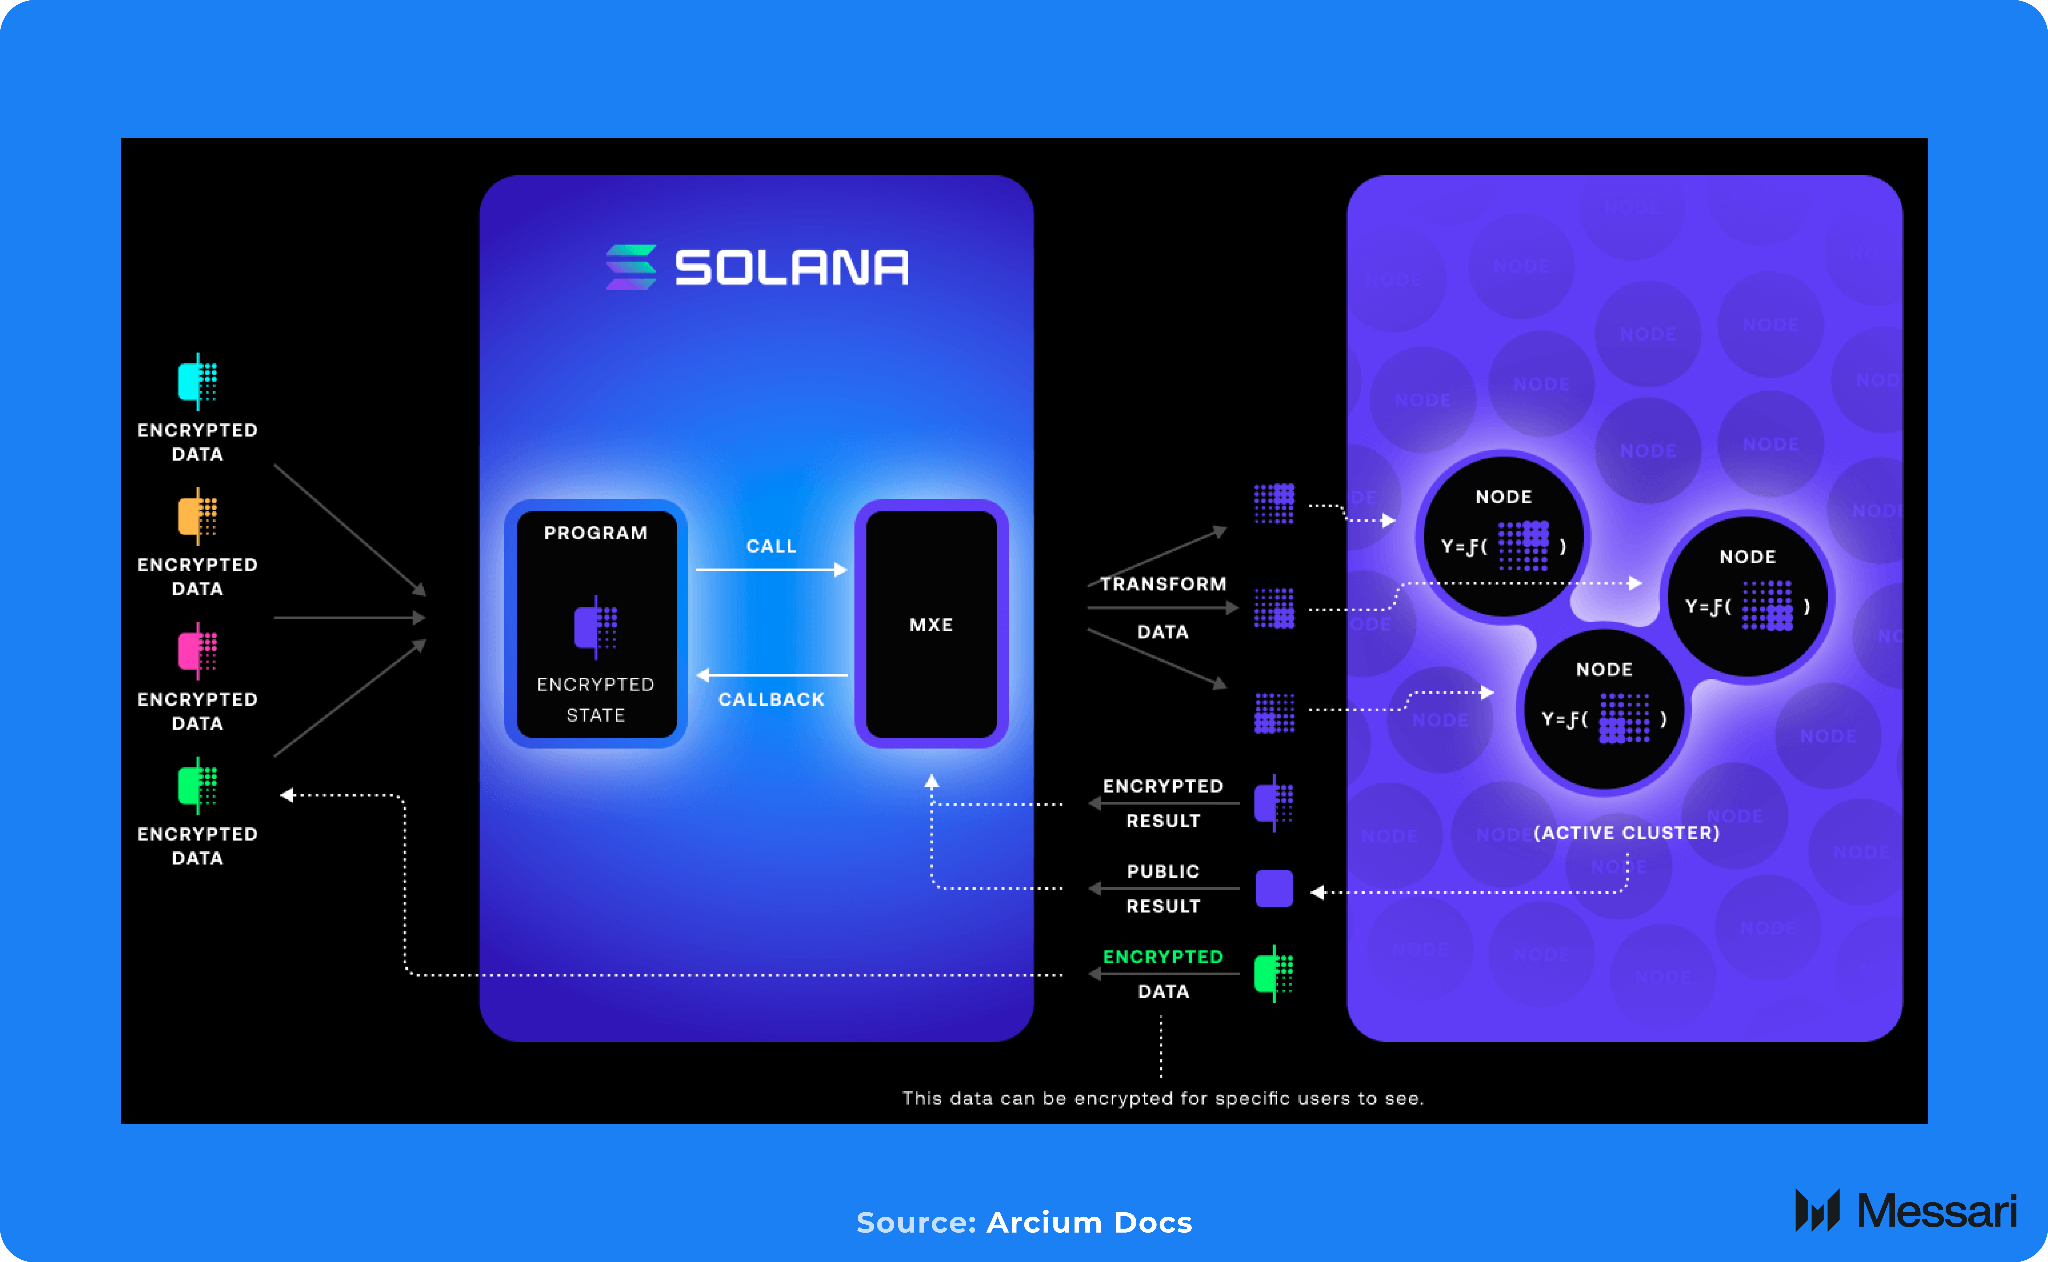
The architecture integrates seamlessly with Solana, which provides the essential data availability and state-consensus layers. Arcium is used by this base layer, handling the sensitive data computation offchain while relying on the base chain for coordination and verification.
Arcium is built on Multi-Party Computation (MPC) because it offers a more flexible, trust-minimized approach to encrypted computing than existing alternatives. Zero-knowledge systems and Fully Homomorphic Encryption (FHE) excel at preserving privacy and verifiability but often face significant performance overhead and limited practicality when applied to arbitrary, stateful computation at scale. Trusted Execution Environments (TEEs), while performant, introduce reliance on hardware vendors and single execution domains, creating centralized trust assumptions. MPC avoids these trade-offs by distributing trust across multiple independent nodes, enabling arbitrary encrypted computation without specialized hardware or expensive proof generation, while preserving decentralization and composability.
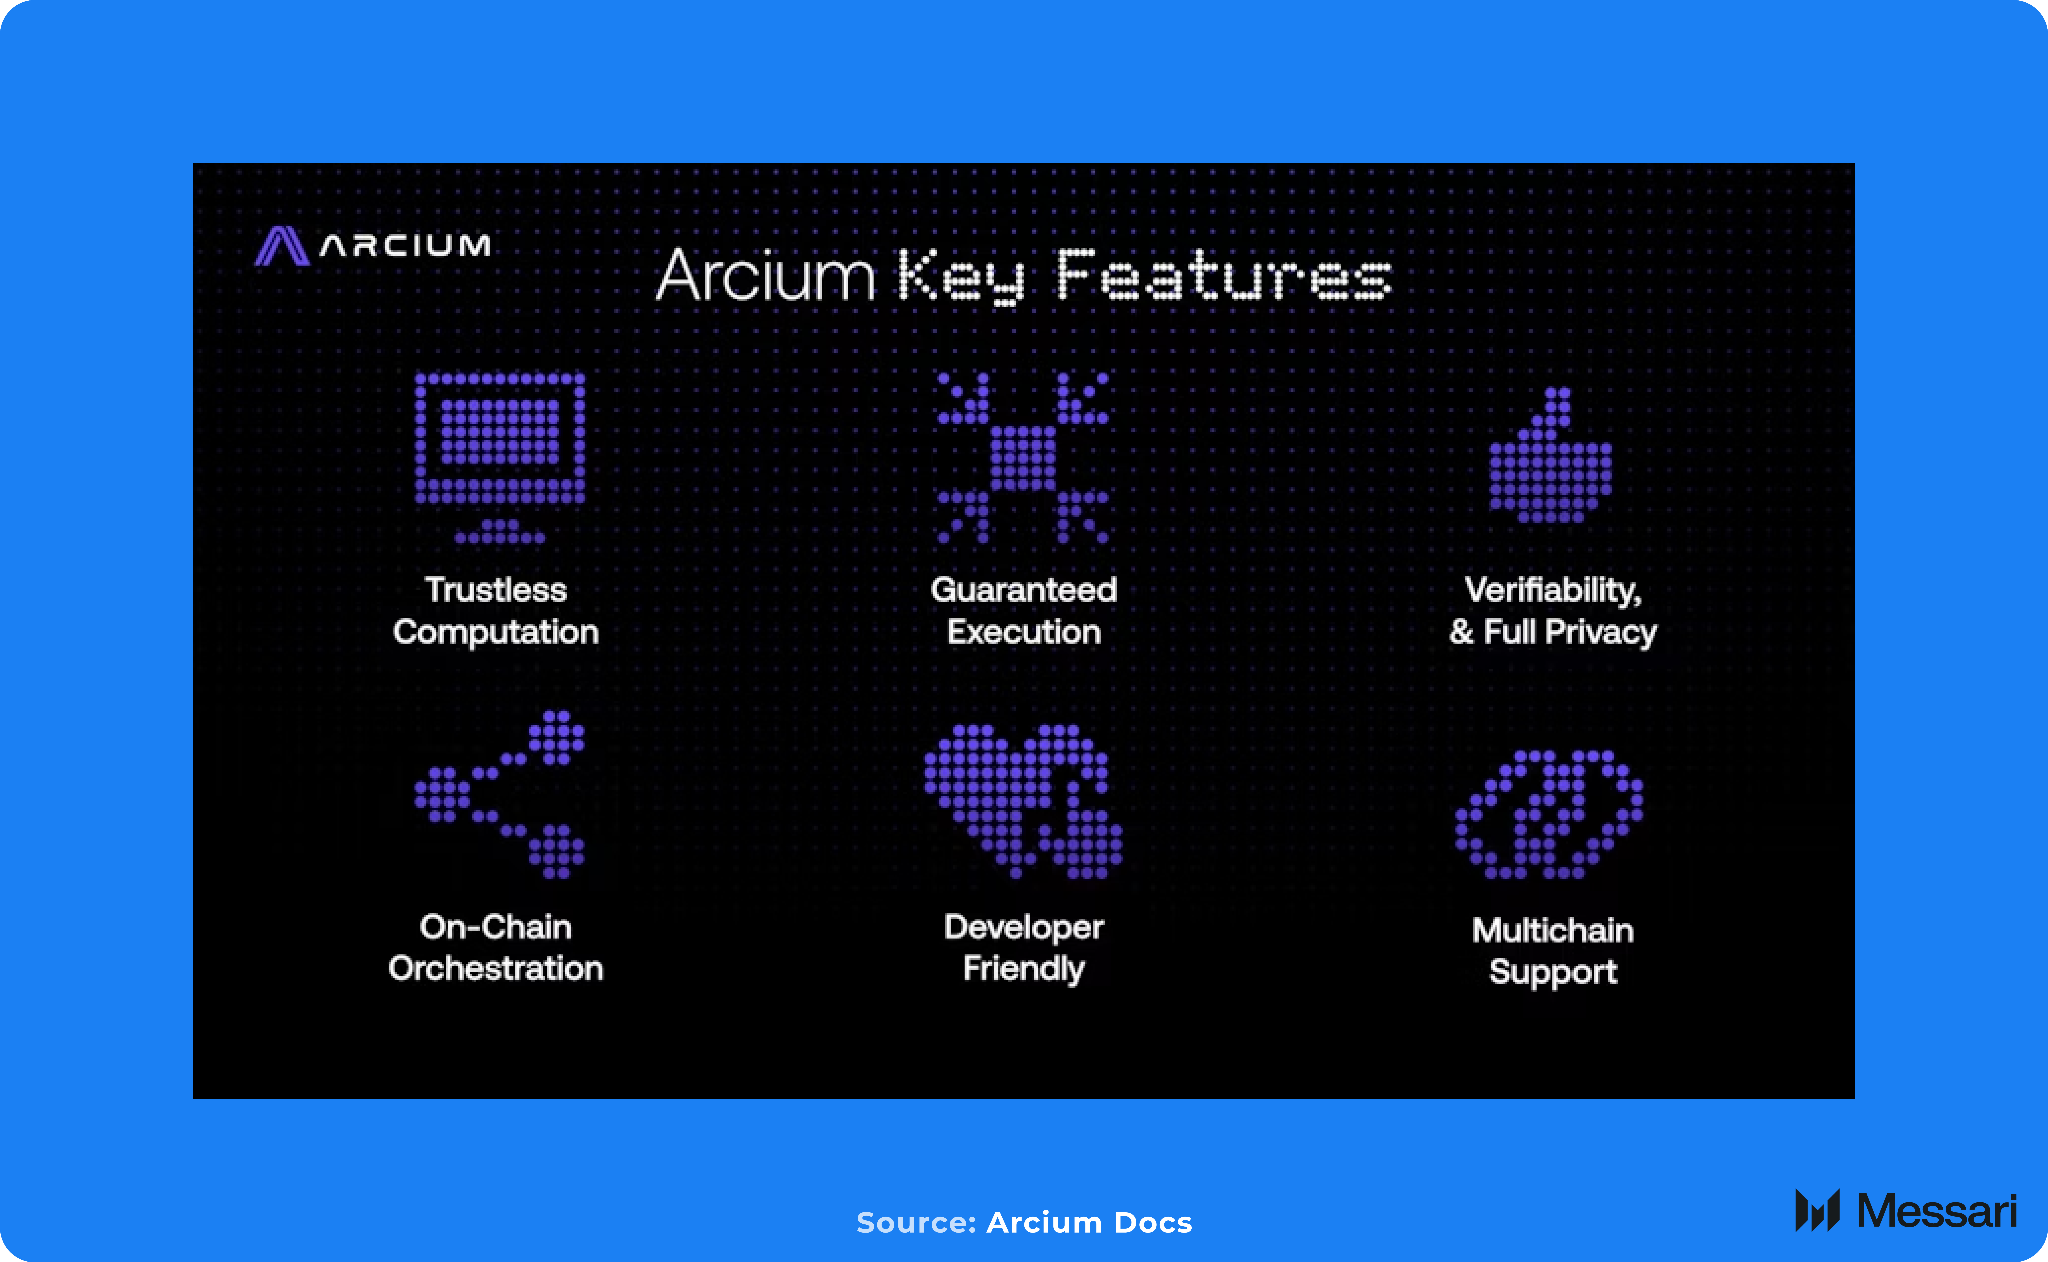
Encrypted Computing: The Arcium Network is fully trustless through its Multi-Party Execution Environments (MXEs), which allow nodes to jointly perform arbitrary computations on encrypted data. At no point is the underlying data exposed, enabling secure and encrypted processing across a decentralized set of operators.
Guaranteed Execution: Arcium ensures reliable and correct computation through a blockchain-based orchestration system. All MXE participants commit collateral via staking, and the protocol uses slashing to penalize misbehavior or deviation from expected execution rules. This mechanism guarantees that every assigned computation is completed correctly and deterministically.
Verifiability and Privacy: Arcium supports public verifiability while maintaining complete data encryption. Anyone can audit the correctness of a computation’s output, yet the inputs remain encrypted throughout the entire process. This pairing of verifiability and privacy is central to Arcium’s design.
Onchain Orchestration: Arcium leverages Solana as its orchestration layer, managing task scheduling, node compensation, staking, and performance incentives. Execution guarantees, penalties, and coordination logic are enforced fully onchain, ensuring transparency and trust minimization.
Developer-friendly Tooling & SDKs: Arcium offers both a graphical interface for non-technical users and full SDK integration for developers familiar with Solana tooling. The platform is designed to make complex MPC workflows accessible and easy to deploy.
Multi-Chain Compatibility: While Arcium’s initial orchestration is built on Solana, the protocol is architected to support multiple chains. Over time, Arcium can serve as a universal, encrypted computing layer across various blockchain ecosystems.
Potential Use Cases:
Encrypted DeFi: Enables private trading, hidden order books, shielded positions, and encrypted smart contract logic while maintaining verifiable execution guarantees. Consider a DeFi protocol executing a liquidation or rebalancing strategy. Onchain execution would reveal the strategy logic and timing. Using Arcium, the strategy inputs are encrypted, executed privately across an MXE, and only the final trade instructions are settled onchain.
Collaborative Data Analytics: Multiple parties can compute aggregated insights on shared encrypted datasets without revealing sensitive data to one another.
Secure AI/ML Compute: Supports encrypted model inference and training, allowing organizations to collaborate on machine-learning workloads while maintaining data privacy. A data provider can submit encrypted inputs to an Arcium-powered inference model. The model runs inside an MXE, producing an output without exposing the underlying data to the model owner or node operators.
Trustless Dark Pools & Private Marketplaces: Facilitates private auctions, trading venues, or bidding systems where identities and bids remain hidden while execution remains provably correct.
Enterprise Privacy Applications: Institutions in finance, healthcare, and supply chain can leverage Arcium’s MPC network for secure processing of sensitive data under decentralized trust assumptions.
Founding Team
Arcium was founded by a team with deep experience in distributed systems, cryptography, MPC, and secure enclaves. The project began as an effort to bring privacy-first computation to crypto, avoiding trusted hardware and instead relying on well-studied cryptographic protocols. Over time, the team expanded its approach to incorporate flexible developer tooling, a virtual machine for encrypted compute, and a network of nodes capable of collaboratively executing encrypted tasks.
The team’s co-founders are as follows:
Yannik Schrade (Co-founder & CEO): Yannik has a strong background in cryptography and engineering. His early success includes developing Shiftscreen, an iOS app with over 100,000 paying users, and he holds a foundation in computer science and mathematics. He has also studied law, which has given him a multidisciplinary perspective on both technical and regulatory issues. As CEO, he drives Arcium’s technical strategy, particularly in the area of MPC, and sets the overall vision for encrypted computing.
Nico Schapeler (Co-founder & CTO): Nico comes from a background in mathematics and computer science at the Technical University of Munich and has been working at the intersection of cryptography and blockchains for nearly a decade. Notable prior work includes TEEs (trusted execution environments) for key material, high-performance hash algorithm implementations, and ZK technology for onchain privacy. At Arcium, he leads all technical aspects from cryptographic research to protocol implementation.
Julian Deschler (Co-founder & CSO): Julian studied engineering and economics at the Technical University of Munich and discovered Bitcoin and Ethereum in 2016, pivoting into decentralized technologies. He spent two years in finance and banking before moving fully into Web3. He also has experience in entrepreneurship and startup boards (e.g., START Munich). As Chief Strategy Officer, Julian shapes Arcium’s strategic direction and supports growth in the decentralized compute ecosystem.
Lukas Steiner (Co-founder & COO): Lukas joined the founding group after meeting Yannik, Nico, and Julian at a hacker house. He brings operational and development experience, including a stint at a fintech startup in Zürich, where he reported to a former McKinsey CFO, as well as an interest in AI through a GPT-3-based SaaS application that was later acquired.
Mainnet Alpha
Arcium’s Mainnet Alpha represents the project’s first production-grade deployment, offering a permissioned MPC network with controlled permissions. The Alpha introduces a curated set of compute nodes that can execute encrypted workloads in a stable environment, serving as a bridge between the experimental testnet and a fully permissionless mainnet.
Key features of Mainnet Alpha include:
Support for production-ready MPC computations
Initial partner integrations, including workflows for DeFi, AI, and private data processing
A developer SDK enabling teams to write, submit, and verify encrypted computations
A monitored environment to ensure network stability and security during early adoption
Guardrails around node membership and workload execution to prevent misbehavior during the rollout phase
The Alpha release is focused on reliability and usability rather than full decentralization. It is designed to allow early adopters to experiment with real applications, gather performance benchmarks, and provide feedback on the developer experience before the protocol moves toward permissionless operation. Full mainnet launch and TGE planned for Q1 2026.
Umbra
One notable team building on top of Arcium is Umbra. Umbra is developing fully private transactions, where not only are balances and amounts hidden, but the sender and recipient are hidden, too. Umbra uses Arcium’s MPC and zero-knowledge proofs (ZKPs) to achieve fully private transactions. By using Arcium’s tech stack, Umbra is able to move critical computation into Arcium’s Multi-Party Execution Environments (MXEs). This allows Umbra to keep inputs and intermediate states private, while still settling final outcomes onchain in a way that remains auditable. In effect, Arcium acts as Umbra’s encrypted execution layer, enabling privacy at the level of computation rather than just transfers.
In October 2025, Umbra held its ICO on MetaDAO, raising over $155 million in commitments. This is one of the largest ICOs on Solana to date, signaling great demand for privacy and Arcium-related projects. Umbra is expected to go live in February.
C-SPL Standard
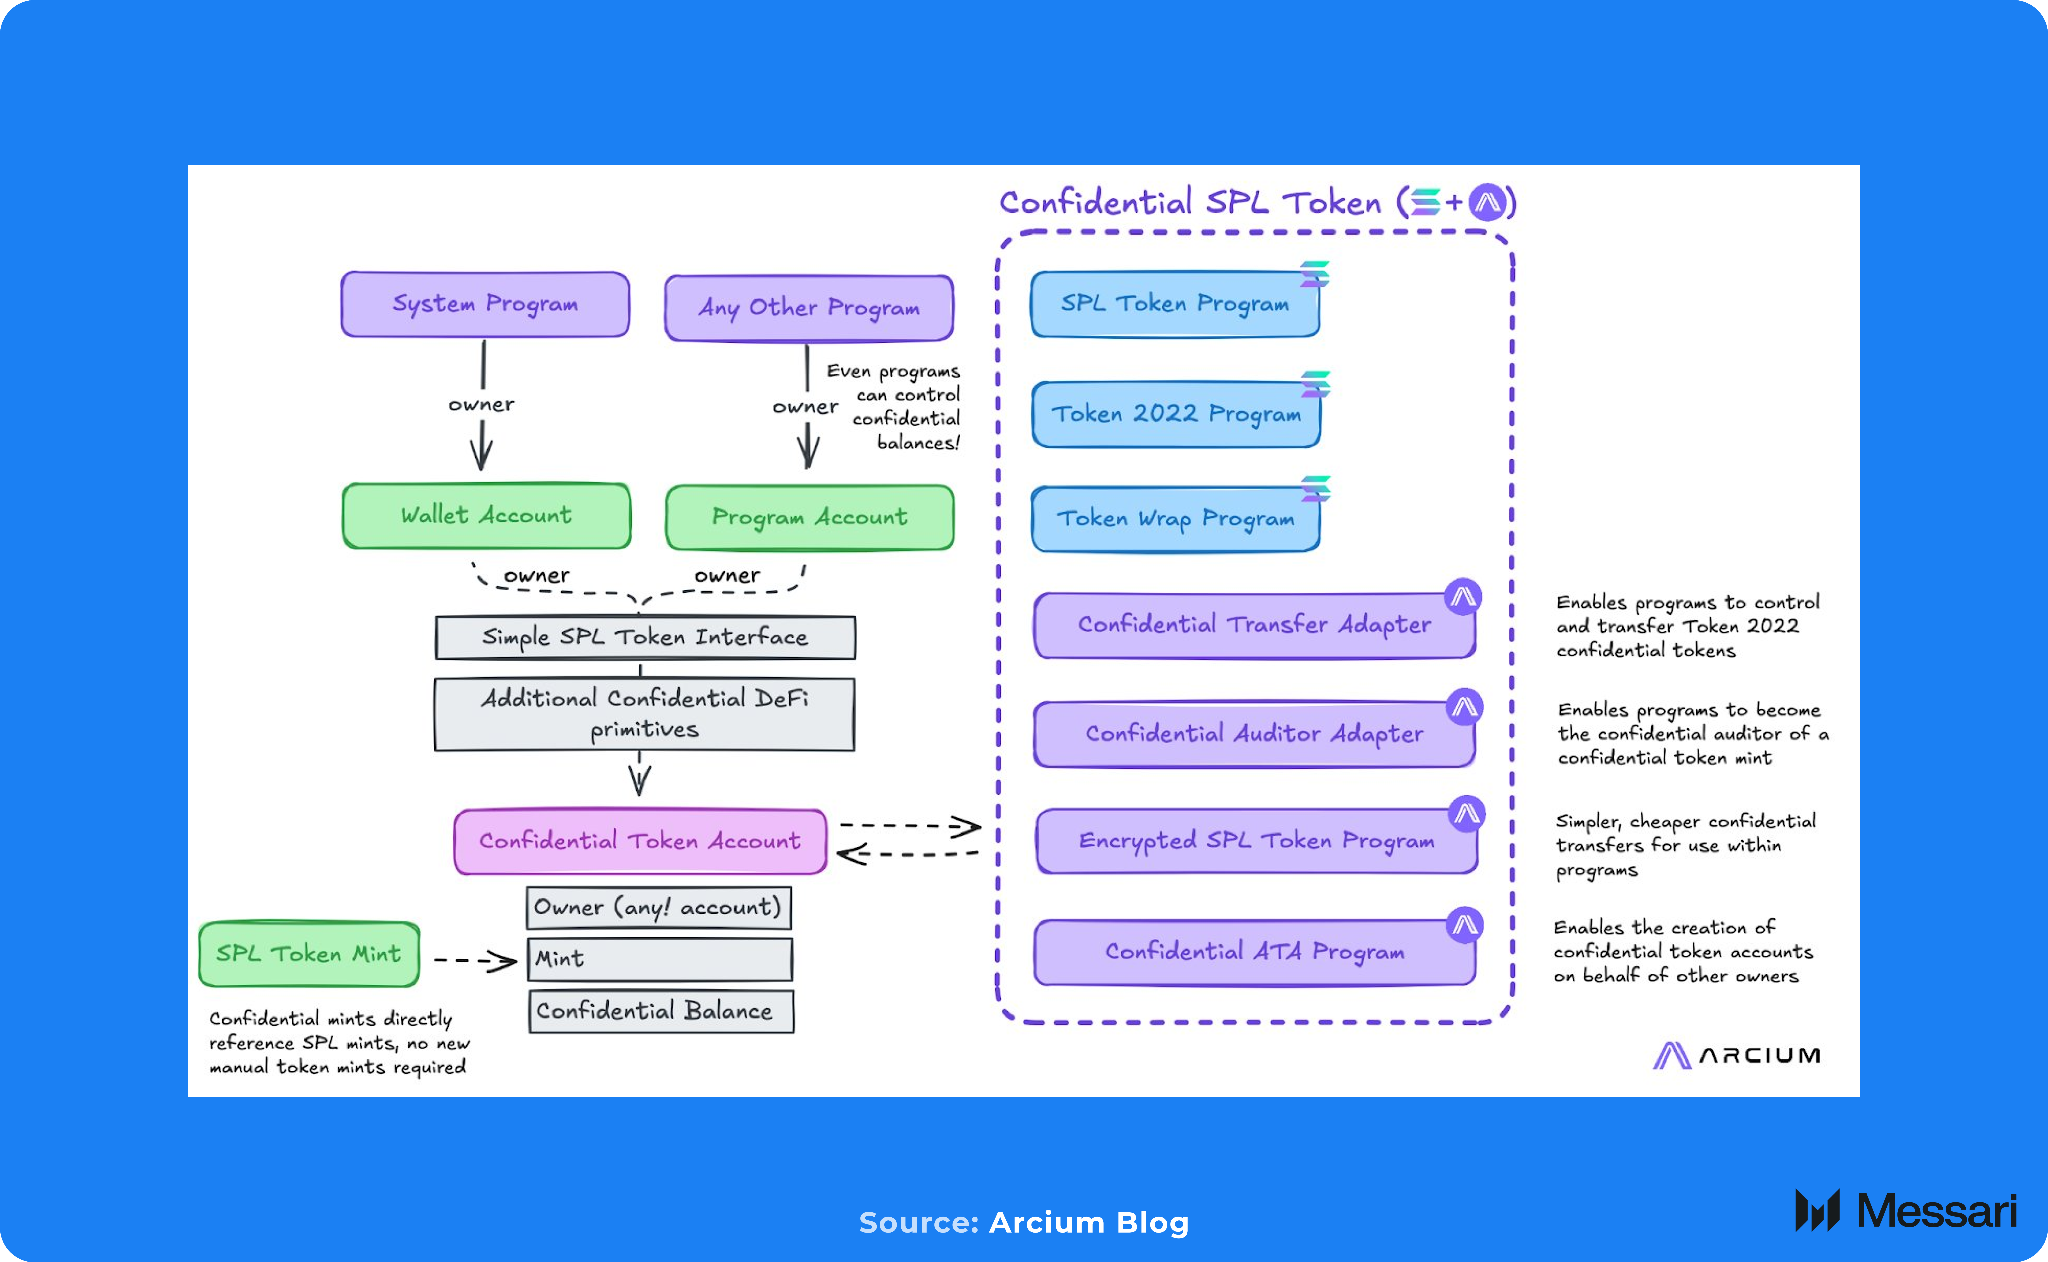
In Q1 2026, Arcium will launch its Confidential SPL token standard, an extension of Solana’s SPL token model that enables programmable, privacy-preserving logic, rather than just private balances or transfers. While existing Solana standards, such as Token-2022, introduce confidentiality at the transaction level by hiding balances or transfer amounts, C-SPL focuses on enabling confidential computation over token state. In practice, this allows token-related logic to be executed inside Arcium’s confidential compute network, with only the final, verified outcome committed back onchain.
At a high level, C-SPL acts as a bridge between Solana’s transparent execution environment and Arcium’s Multi-Party Execution Environments (MXEs). Token state or parameters can be securely referenced by a confidential computation, processed privately across multiple nodes, and returned as a verifiable result without revealing sensitive inputs. This design enables use cases that extend beyond private transfers, such as confidential DeFi strategies, hidden order logic, private auctions, or token mechanics where rules or parameters must remain undisclosed until execution is complete.
Importantly, C-SPL preserves Solana’s composability while expanding its privacy surface. The onchain components remain auditable and deterministic, while sensitive logic is abstracted into Arcium’s trustless compute layer.
Testnet Traction
Arcium’s public testnet went live on May 1, 2025, marking the project’s first large-scale deployment of its MPC-powered encrypted compute network. The testnet served as a proving ground for validating node stability, developer workflows, and application performance ahead of Mainnet Alpha.
The testnet supported a globally distributed network of more than 3,000 Arx Nodes, demonstrating the protocol’s capacity to coordinate MPC workloads at scale. Developer engagement was similarly strong, as teams deployed over 30 applications that leveraged Arcium’s encrypted compute primitives. The ecosystem generated over 300 hackathon submissions, reflecting early experimentation across DeFi, AI/ML, data collaboration, and privacy-preserving consumer applications.
Arcium’s emphasis on simple developer onboarding through the Arcis framework helped accelerate testnet adoption. Many teams rapidly shipped “demo-ready” prototypes that showcased how encrypted offchain logic can extend existing blockchain use cases. Featured examples from the public testnet include:
Private Orderflow & Matching Engines: Prototypes demonstrating encrypted order routing, encrypted RFQs, and sealed-bid execution flows for DeFi venues. In a sealed-bid auction, bids are submitted encrypted to Arcium, evaluated inside an MXE, and the winning bid is revealed without exposing losing bids or participant identities.
AI Inference with Encrypted Inputs: Applications running inference on private data using Arcium’s hybrid MPC–FHE execution model, enabling model owners and data providers to collaborate without exposing sensitive information.
Confidential Data Rooms & Sharing Pipelines: Workflows enabling multiple parties to compute aggregated insights on encrypted datasets, relevant for institutions handling regulated or proprietary information.
Identity & Access Control Primitives: Early demos using Arcium’s compute layer to manage private attestations or permissioning logic without revealing user data.
The testnet validated Arcium’s core design assumptions around encryption, verifiability, and network-level execution guarantees. High node participation, sustained developer engagement, and the breadth of early applications suggest strong foundational demand for a decentralized, encrypted compute layer. These learnings directly informed the design constraints and operational safeguards introduced in Mainnet Alpha.
Closing Summary
Arcium is building a decentralized, encrypted compute network that supports the next generation of privacy-preserving applications. The protocol’s architecture aims to eliminate the trade-offs that have historically limited trustless computation by offering both encryption and verifiability at scale. The public testnet, launched on May 1, 2025, provided a strong early signal of market demand, attracting over 3,000 globally distributed nodes and a broad range of developer experimentation, from encrypted order flow engines to private AI inference and institutional data-sharing pipelines.
Mainnet Alpha is Arcium’s first production-grade environment, prioritizing reliability, controlled node participation, and stable execution guarantees. This phase allows partners and builders to deploy real workloads, benchmark performance, and refine applications ahead of a permissionless mainnet. With continued development of the Arcis framework, enhancements to deployment on Solana, and growing interest from teams exploring private computation, Arcium is positioned to become a core infrastructure layer for encrypted offchain logic. The path to full mainnet decentralization will determine how effectively Arcium can scale its MPC network while preserving trust-minimized guarantees, but early momentum indicates that encrypted compute is becoming a critical component of the Web3 stack.
This report was commissioned by Arcium Network. All content was produced independently by the author(s) and does not necessarily reflect the opinions of Messari, Inc. or the organization that requested the report. The commissioning organization may have input on the content of the report, but Messari maintains editorial control over the final report to retain data accuracy and objectivity. Author(s) may hold cryptocurrencies named in this report. This report is meant for informational purposes only. It is not meant to serve as investment advice. You should conduct your own research and consult an independent financial, tax, or legal advisor before making any investment decisions. Past performance of any asset is not indicative of future results. Please see our Terms of Service for more information.
No part of this report may be (a) copied, photocopied, duplicated in any form by any means or (b) redistributed without the prior written consent of Messari®.
Matthew is a Research Analyst in Protocol Research. He graduated from MIT with a Master's and Bachelor's in Comp Sci, Economics, and Data Science where he wrote his thesis on DeSoc. Matthew also has previous experience as an Analyst at Goldentree's crypto fund.
Matthew is a Research Analyst in Protocol Research. He graduated from MIT with a Master's and Bachelor's in Comp Sci, Economics, and Data Science where he wrote his thesis on DeSoc. Matthew also has previous experience as an Analyst at Goldentree's crypto fund.