Zama is a chain-agnostic confidentiality layer that enables smart contracts on existing blockchains to compute directly on encrypted data using Fully Homomorphic Encryption (FHE), without breaking composability.
The Zama Protocol separates execution from encrypted computation via an offchain coprocessor architecture and threshold decryption, allowing confidential applications to scale without impacting host chain performance while preserving public verifiability.
Zama’s launched its utility token through a a sealed-bid Dutch auction, intentionally using the Zama Protocol itself to keep bids confidential, serving as both a fair distribution mechanism and a live stress test of the protocol’s production-grade confidentiality guarantees.
Zama’s roadmap emphasizes scalability and long-term resilience, targeting hardware-accelerated FHE, ZK-rollup-based Gateway, broader operator participation, and post‑quantum cryptography by keeping its FHE and MPC components quantum‑resistant while replacing the current, non‑PQ ZKPoK with a lattice‑based zero‑knowledge scheme.
Introduction
Public blockchains are built on the principle of radical transparency. Every transaction, balance, and state transition is globally visible by default. This design has been foundational to minimizing trust and ensuring verifiability, but it also introduces structural risks that limit blockchain adoption beyond crypto-native use cases. For enterprises, institutions, and end users handling sensitive data, full transparency exposes proprietary information, counterparties, business logic, and financial positions to competitors, adversaries, and onchain surveillance.
The industry has increasingly recognized that confidentiality is not optional infrastructure but a prerequisite for the next phase of onchain adoption. However, existing privacy solutions often introduce significant friction. They require new execution environments, specialized developer expertise, fragmented tooling, or trade-offs between composability, performance, and security. As a result, privacy has remained siloed rather than natively embedded into mainstream blockchain development.
Zama aims to address this gap by providing confidentiality as a programmable, onchain primitive. Built around Fully Homomorphic Encryption (FHE), Zama enables smart contracts to operate directly on encrypted data, allowing computations to be performed without revealing the underlying values. From the developer’s perspective, Zama functions as plug-and-play infrastructure: applications can add confidential logic without redesigning their architecture, migrating to a new chain, or sacrificing composability with existing onchain systems. For a deeper dive on FHE, here’s the DeCC report.
The protocol introduced its first major open-source milestone with the launch of the Concrete Framework in July 2022. The ecosystem took a massive leap forward in September 2023 with the debut of the fhEVM (Fully Homomorphic Ethereum Virtual Machine), which enabled confidential smart contracts on Ethereum for the first time.
The platform scaled further in December 2024 with the launch of the fhEVM Coprocessor, allowing standard EVM chains to offload private computations without leaving the public chain. In November 2025, Zama acquiredKakarot (KKRT Labs), a Vitalik Buterin-backed zero-knowledge (zk) research and development firm. This strategic acquisition strengthens Zama’s technical capabilities in blockchain scalability and validity proofs, enabling the company to integrate modular ZK-based architectures that complement its existing FHE infrastructure.
Technology
Overview
The Zama Confidential Blockchain Protocol (Zama Protocol) is a cross-chain confidentiality layer that enables the direct issuance, management, and execution of confidential assets on existing public blockchains. Rather than introducing a new Layer-1 (L1) or Layer-2 (L2), the protocol integrates on top of existing chains, allowing DeFi protocols to operate where liquidity is, and users and developers to access confidential applications without the need for bridging or migrating ecosystems.
At its core, the protocol is powered by FHE, which enables computation directly on encrypted data. This allows transaction inputs and onchain state to remain end-to-end encrypted, meaning sensitive data is never revealed, including to node operators, while still remaining publicly verifiable. Smart contracts can execute on encrypted values and define fine-grained decryption rules, enabling programmable confidentiality where developers control exactly who can access specific data.
Zama’s design preserves composability, allowing confidential smart contracts to interact with both other confidential contracts and standard non-confidential contracts. This ensures confidentiality does not come at the expense of interoperability or developer flexibility.
To complement FHE, the protocol incorporates Multi-Party Computation (MPC) and ZK in targeted roles. MPC is used to decentralize key management and decryption, ensuring no single party controls sensitive cryptographic material while minimizing performance overhead. ZK proofs are used to verify that encrypted inputs are formed correctly, without revealing the underlying data, keeping proofs lightweight and suitable for client-side generation.
Workflow
Building a confidential application with Zama closely mirrors standard EVM development. Developers write smart contracts directly in Solidity and import the fhEVM library, replacing plaintext variables and operations with encrypted equivalents where confidentiality is required. The overall contract structure, tooling, and deployment process remain familiar, lowering the barrier to adding confidentiality to existing applications.
Sensitive application state, such as balances, positions, or votes, is stored onchain in encrypted form and updated through encrypted computation. Contracts operate on this encrypted state natively, enabling confidentiality to persist across transactions rather than being limited to isolated transfers. This allows developers to build fully confidential primitives such as tokens, predictive markets, governance systems, or auctions without redesigning their application architecture.
User inputs are encrypted client-side and verified onchain before execution, ensuring correctness while keeping the encryption and proof generation largely invisible to end users. Zama’s Relayer SDK abstracts this process, allowing confidential dApps to deliver user experiences comparable to standard web and onchain applications.
Zama’s workflow centers on programmable access control, enabling applications to enforce full encryption or selective disclosure at the protocol level. By extending the EVM with native confidentiality, developers retain existing liquidity and integrations while leveraging audited confidential contracts.
Architecture
Symbolic Execution
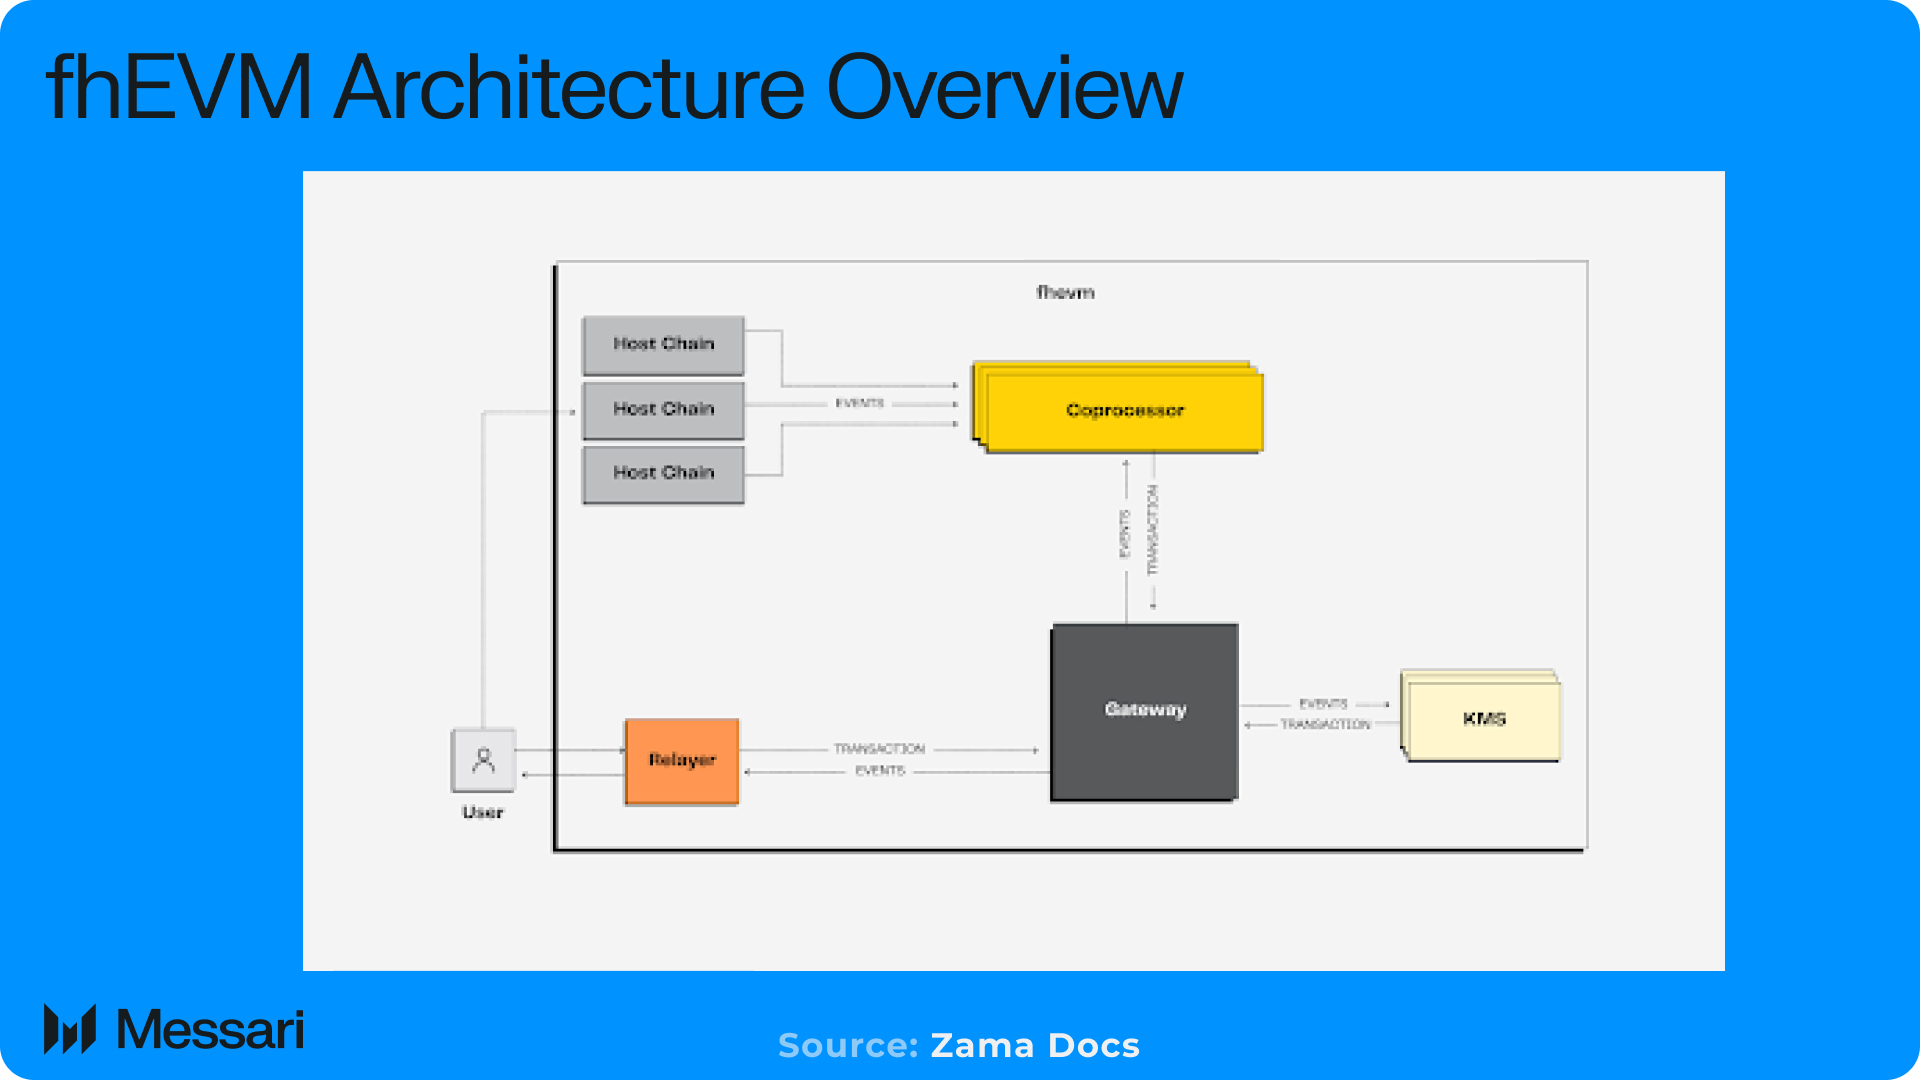
Because existing L1s and L2s are not designed to securely manage encryption keys or support heavy encrypted computation within their execution environments, the Zama Protocol separates smart contract execution from confidential computation. When a smart contract calls an FHE operation via the fhEVM library, the host chain does not perform the computation itself. Instead, it records a symbolic reference to the result and emits an event that is picked up by a network of offchain coprocessors.
These coprocessors perform the actual FHE computation in parallel and return the encrypted result, while the blockchain continues executing normally. This design allows confidential applications to coexist with standard transactions without slowing down the underlying chain or requiring protocol-level changes. Encrypted values can be composed and chained like regular variables, with computation latency only becoming relevant when a value must be decrypted.
From a security standpoint, the coprocessor layer is publicly verifiable. Any party can recompute the encrypted outputs to check correctness, and the protocol is designed to evolve toward open participation where coprocessors prove correct execution using cryptographic proofs rather than trusted coordination.
Threshold Decryption
To preserve composability across confidential applications, all encrypted values in the Zama Protocol are generated under a shared public key. Rather than entrusting decryption to a single entity, the corresponding private key is split across multiple independent parties using a threshold multi-party computation scheme, forming the protocol’s key management layer.
Smart contracts explicitly define which users or contracts are permitted to decrypt specific values. When decryption is requested, the Zama Gateway coordinates with the key management parties to produce the plaintext only if the onchain access rules are satisfied. All decryption requests are publicly observable, allowing external verification that decryption events align with the application’s encoded logic.
This approach ensures that no single party can decrypt data unilaterally, while maintaining onchain composability and enforcing confidentiality through smart contract-defined rules rather than offchain trust assumptions.
Scaling
The Zama Protocol is designed to scale horizontally by decoupling encrypted computation from onchain execution and leveraging parallelism at the coprocessor layer. Because FHE operations are not bound to the EVM’s sequential execution model, throughput can increase as additional compute resources are added, provided encrypted values are not part of a strict dependency chain.
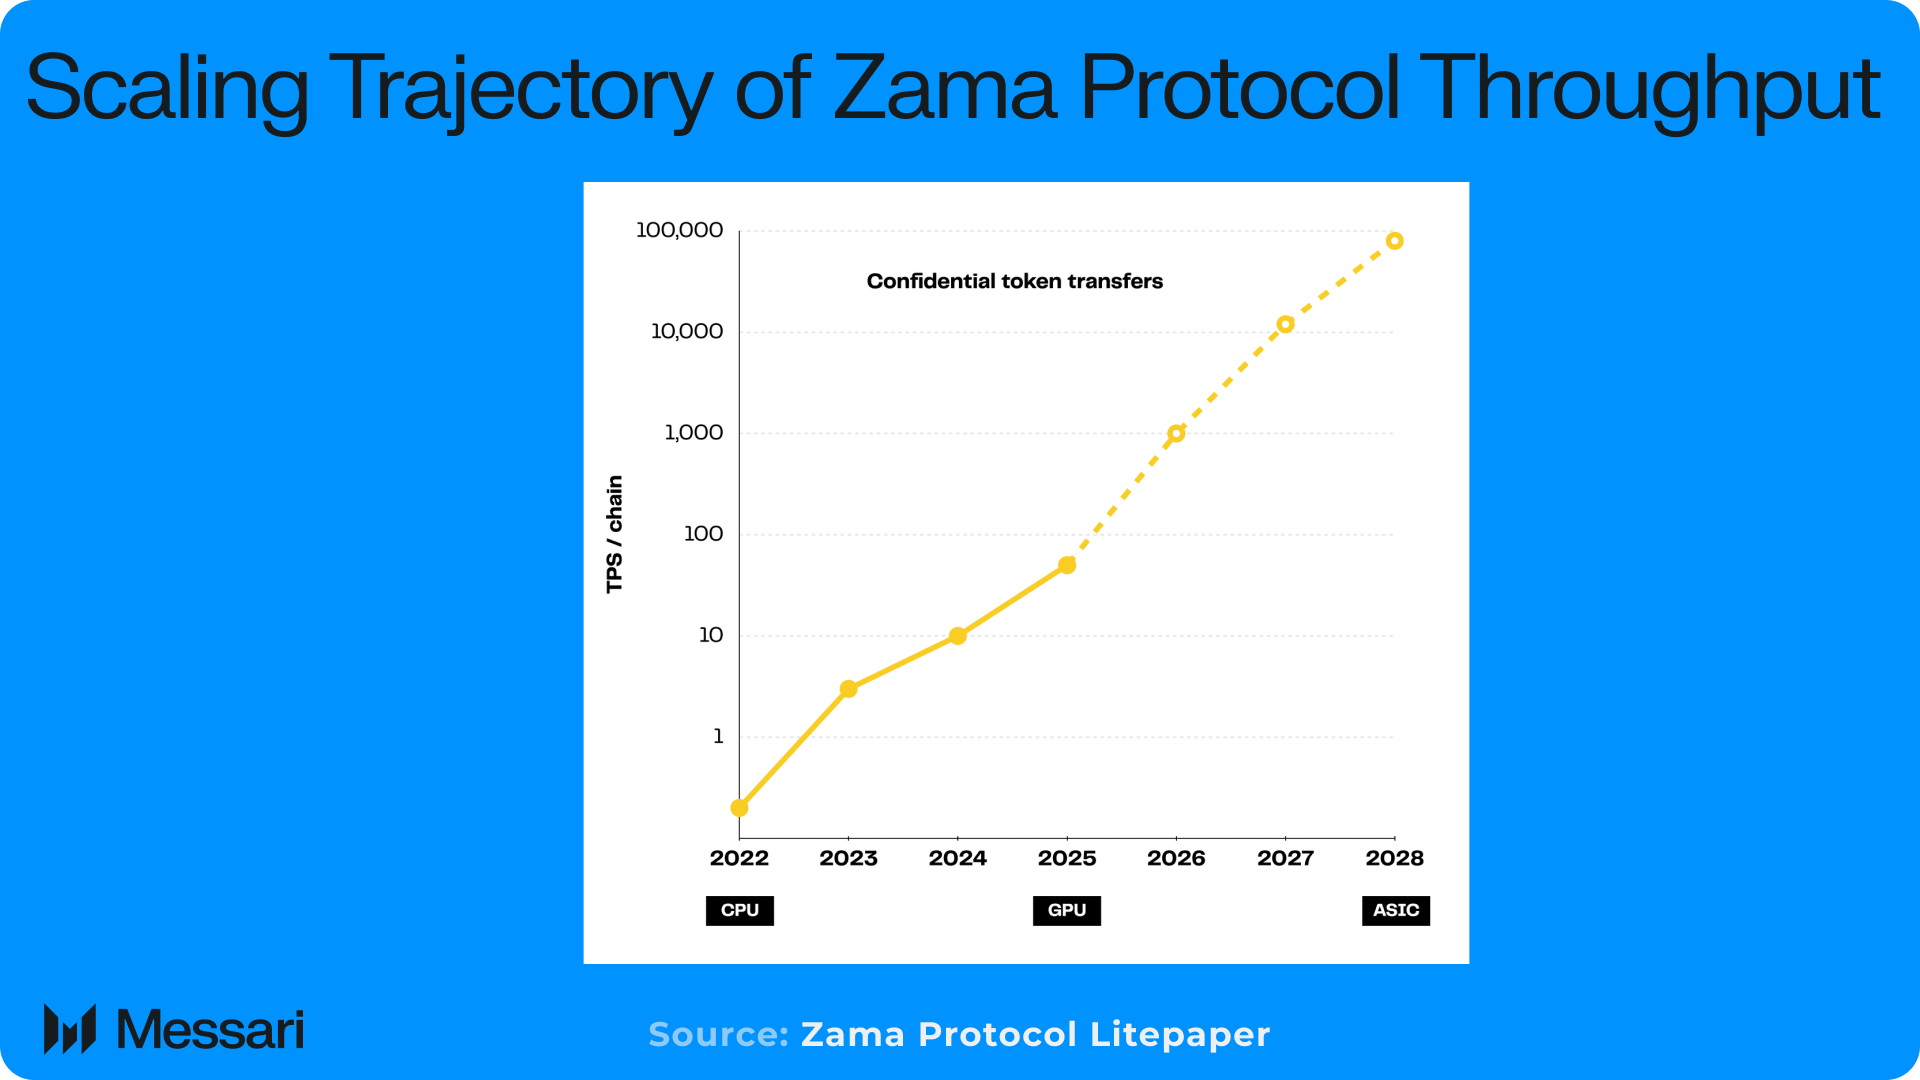
Since early development, Zama has increased encrypted throughput from multiple seconds to execute a transaction to more than 20 transactions per second using CPU-based execution, demonstrating that confidentiality can be supported at meaningful network scale. The roadmap outlines an initial GPU-accelerated deployment on testnet in June 2026, followed by mainnet integration in Q3 2026. With GPU acceleration, expected throughput increases to hundreds of transactions per second per chain, making the system viable for integrated host chains and higher-performance L2 environments.
In the longer term, Zama is developing dedicated hardware accelerators for FHE, targeting orders-of-magnitude increases in throughput. At this stage, performance is framed as a hardware scaling problem rather than a cryptographic limitation, with future gains expected to track improvements in compute infrastructure rather than fundamental protocol changes.
Security
The Zama Protocol adopts a defense-in-depth security model that combines cryptographic guarantees, decentralized execution, and operational safeguards. At the cryptographic layer, all FHE operations are implemented with 128-bit security, exceeding the security assumptions typically used in blockchain-integrated FHE systems. The underlying scheme is post-quantum, offering resilience against known quantum attack vectors. The protocol’s 128-bit post-quantum security places Zama on par with the security standards used by major financial institutions.
Encrypted computation is publicly verifiable. FHE outputs can be independently recomputed to detect incorrect execution, with multiple coprocessors producing signed results to reduce reliance on a single operator. This design mirrors optimistic security models, while adding redundancy through consensus among operators. Over time, the protocol aims to further harden this layer through cryptographic proofs of correct execution.
Key management and decryption rely on a robust threshold MPC system. The protocol tolerates up to one-third malicious participants while still guaranteeing correct outputs. MPC execution is additionally isolated within secure hardware enclaves, providing protection against key exfiltration and enabling verifiable software attestation.
Operational risk is mitigated through the selection of reputable, publicly identifiable genesis operators whose broader economic exposure extends beyond the protocol itself. Misbehavior can be challenged through governance-based slashing, allowing flexible and context-sensitive responses rather than rigid automated penalties. Finally, the protocol has undergone an extensive third-party security review, with ongoing audits conducted by Trail of Bits and Zenith.
Tokenomics
ZAMA is the utility token of the Zama Protocol. The token is used to pay encryption and decryption fees, stake or delegate to operators, and help secure FHE coprocessors and key management nodes, with full functionality live ahead of launch. Zama launched its utility token through a sealed-bid Dutch auction, deliberately using the Zama Protocol to keep bids confidential. This served both as a fair distribution mechanism and as a live stress test of the protocol’s production-grade confidentiality guarantees.
Fee Model
The Zama Protocol employs a volume-based fee model, designed for predictability and affordability, where all protocol fees are priced in USD and settled in ZAMA tokens. Deploying confidential applications is free and permissionless, with fees applied only to three core operations: verifying ZKPs for encrypted inputs, decrypting ciphertexts, and bridging encrypted values across chains.
The model incentivizes high-volume activity through a tiered discount system where fees per operation decline based on a user’s activity over the previous 30 days. A confidential token transfer, which typically requires one proof verification and three decryptions, will cost less than $0.01 for high-volume participants. This structure enables developers and relayers to model costs in USD and charge sponsor fees for end-users.
Staking Rewards
Operators must stake ZAMA tokens to participate in running the Zama Protocol and qualify for staking rewards. Running the protocol involves operating specialized nodes that either execute confidential computation or manage threshold key custody and decryption. Token distributions are minted according to an inflation schedule (5% initially), adjustable through governance. Rewards are allocated by operational role: Coprocessors receive 8% of total rewards across 5 operators, while KMS nodes receive 4.6% across 13 operators.
Within each role, rewards are distributed pro rata based on the square root of each operator's stake, so compensation scales with contribution but flattens for very large positions. For example, a node staking 400 million tokens only earns twice the rewards of a node staking 100 million, rather than four times as much. Each operator retains discretion over the distribution of rewards to their delegators. Token holders unable to operate nodes can delegate their ZAMA to whitelisted operators and participate in staking rewards, with each operator independently determining incentive structures (commission reductions or supplementary rewards).
Governance & Protocol Upgrades
All protocol modifications, including software upgrades, fee structures, and support for additional host chains, require majority approval from active operators. Emergency protocol pausing and spammer blacklisting are exceptions, permitting any single operator to initiate these actions. However, unpausing the protocol or removing blacklisting designations requires multi-signature approval across multiple coprocessors, preventing unilateral reversal.
Roadmap
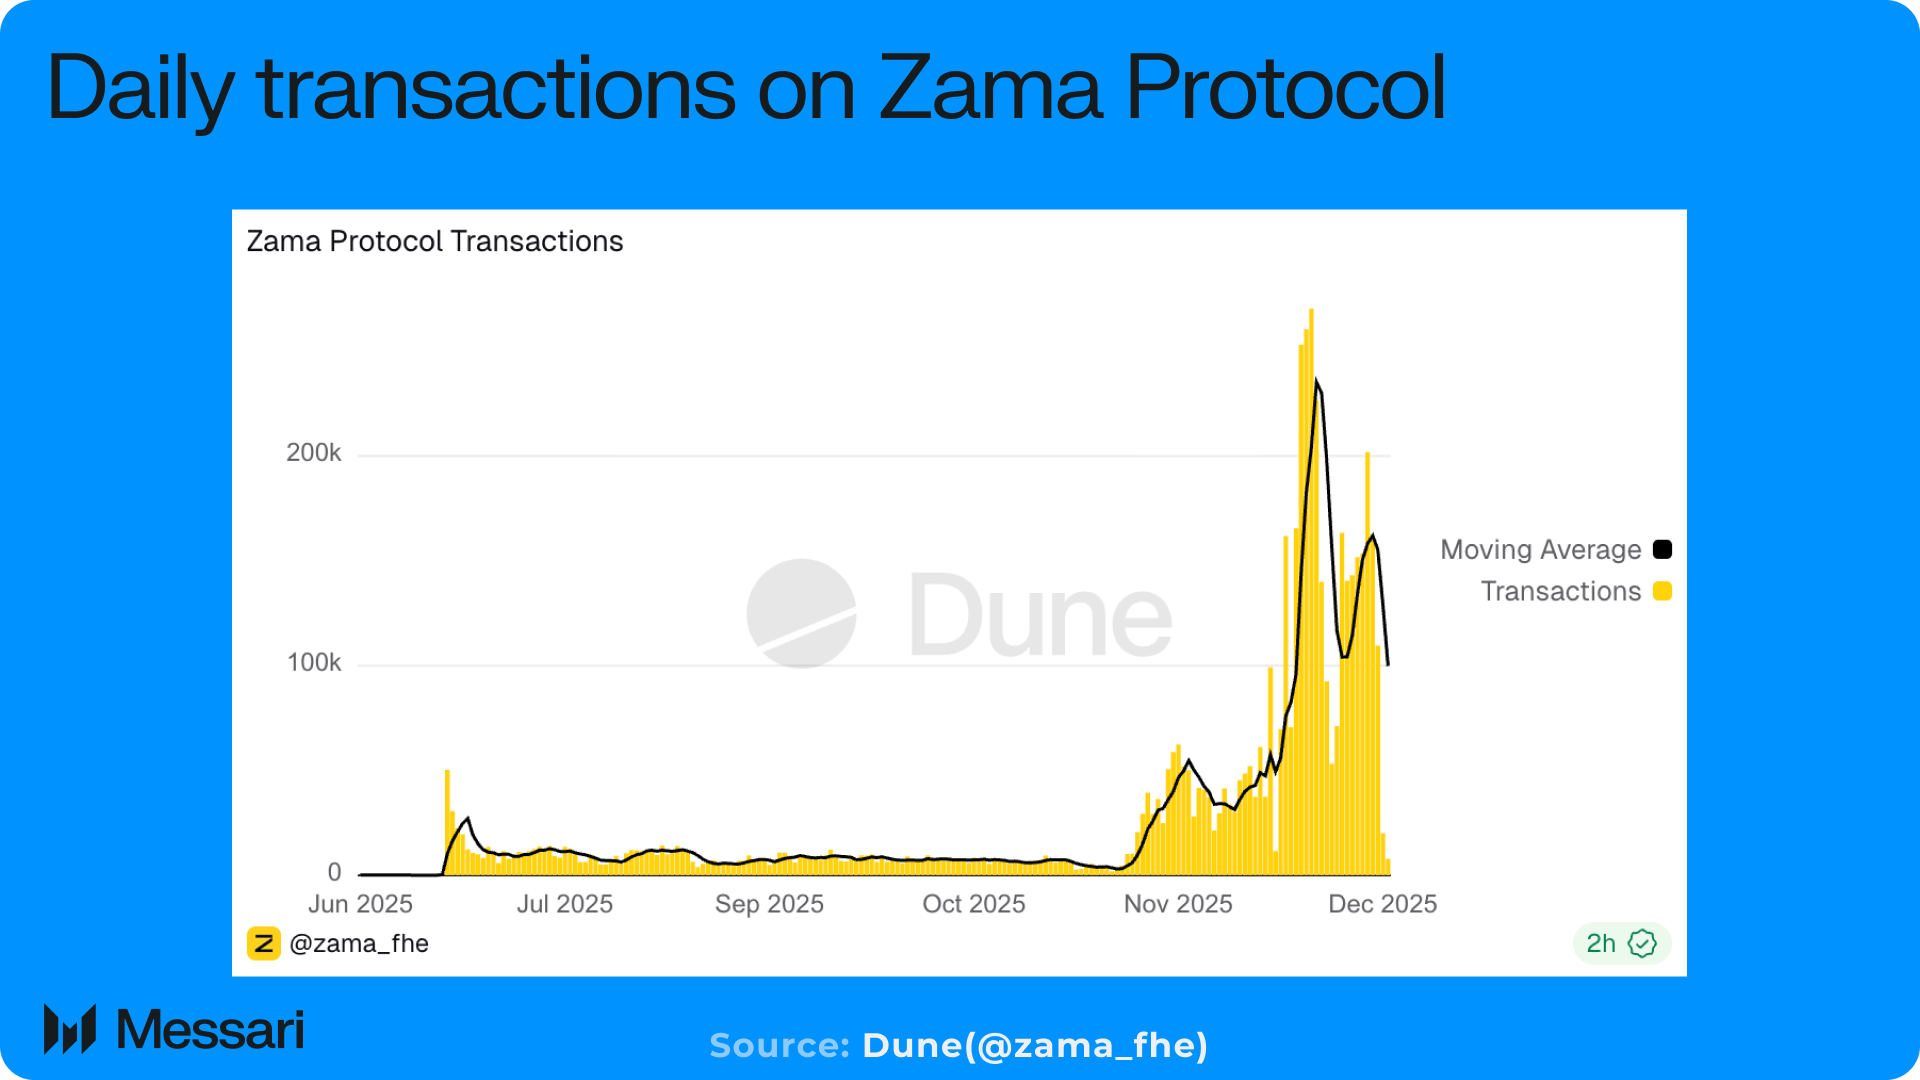
Since the launch of Zama’s first public testnet on July 1, 2025, the protocol has processed more than 6.9 million transactions and supported the deployment of 27,662 confidential contracts built on the Zama stack. Zama has also shielded over $121 million in USDT on Ethereum through its recent public auction.
Zama’s mainnet went live on Dec. 30, 2025, marked by the completion of the first confidential stablecoin transfer (cUSDT) on Ethereum. Shortly after launch, Zama conducted the public ZAMA token sale via a sealed-bid Dutch auction on Ethereum. Unlike a conventional token sale, the auction is intentionally designed to stress-test the Zama stack in production, with the protocol itself used to keep participant bids confidential through FHE.
Looking ahead, Zama’s roadmap is anchored around three priorities: scalability, security, and post-quantum resistance. On scalability, the team is targeting long-term throughput of up to 100,000 transactions per second through a combination of cryptographic and architectural improvements. In parallel, Zama is collaborating with hardware manufacturers on FHE-specific ASICs, targeting 100–1,000x performance gains similar to those achieved in Bitcoin mining, with early hardware expected in the 2027–2028 timeframe. At the protocol layer, the Gateway is expected to migrate from an optimistic rollup to a ZK-rollup architecture, enabling tens of thousands of transactions per second with sub-100 millisecond latency.
On security, Zama plans to strengthen its Key Management System by integrating zero-knowledge proofs into its multi-party computation workflows, allowing onchain verification of individual node correctness rather than relying primarily on hardware trust assumptions. The protocol also intends to expand MPC committees from 13 nodes to roughly 100, materially improving fault tolerance and decentralization relative to typical MPC deployments.
To support permissionless participation, Zama aims to enable MPC execution within hardware security modules commonly used in traditional finance, reducing reliance on trusted execution environments. In addition, the team is developing ZK-FHE proofs of correctness that would enable a proof-of-work-like execution model, allowing any operator to perform FHE computations by submitting verifiable proofs and removing the need for centralized coprocessor selection.
From a post-quantum perspective, Zama’s FHE and MPC components are already quantum-resistant, while its zero-knowledge proofs are expected to migrate to lattice-based post-quantum schemes over time. However, end-to-end quantum resilience will remain partially dependent on host chains such as Ethereum and Solana adopting post-quantum signature schemes at the base layer.
Closing Summary
Zama addresses a structural limitation of public blockchains by introducing confidentiality as a native, programmable primitive rather than an external add-on. By integrating directly with existing L1s and L2s, the protocol allows developers to execute smart contracts on encrypted data without breaking composability or fragmenting liquidity. Early signals are tangible, with sustained testnet usage, a mainnet launch marked by live confidential stablecoin transfers, and a token model that ties economic value to concrete protocol usage rather than abstract governance.
The remaining challenge is execution at scale. Zama’s roadmap encompasses significant cryptographic, architectural, and hardware-level upgrades, alongside a gradual shift toward broader operator participation. Delivery on these fronts will determine whether the protocol becomes a standard component of onchain infrastructure for applications that require confidentiality, regulatory alignment, and data protection by default.
This report was commissioned by Zama Switzerland AG. All content was produced independently by the author(s) and does not necessarily reflect the opinions of Messari, Inc. or the organization that requested the report. The commissioning organization may have input on the content of the report, but Messari maintains editorial control over the final report to retain data accuracy and objectivity. Author(s) may hold cryptocurrencies named in this report. This report is meant for informational purposes only. It is not meant to serve as investment advice. You should conduct your own research and consult an independent financial, tax, or legal advisor before making any investment decisions. Past performance of any asset is not indicative of future results. Please see our Terms of Service for more information.
No part of this report may be (a) copied, photocopied, duplicated in any form by any means or (b) redistributed without the prior written consent of Messari®.
Alice is a Research Analyst on the Protocol Services team. She previously worked as a Research Analyst at The Block and was an Investment Intern at Variant Fund. Alice graduated from Northwestern University, where she studied Economics.
Alice is a Research Analyst on the Protocol Services team. She previously worked as a Research Analyst at The Block and was an Investment Intern at Variant Fund. Alice graduated from Northwestern University, where she studied Economics.