Quantus Network is a Proof-of-Work Layer-1 built on Substrate, with post-quantum cryptography at the protocol level.
~$3.0 trillion in assets rely on Elliptic-Curve Cryptography, leaving them vulnerable to the threat of quantum computers.
Quantus solves quantum-secure scaling concerns with ZK aggregation, utilizing the Poseidon2 hash function in combination with Plonky2’s recursion to aggregate proofs into a single succinct proof for scalability.
Quantus’s reversible transactions and High-Security Accounts provide a more forgiving user experience while maintaining cryptographic security.
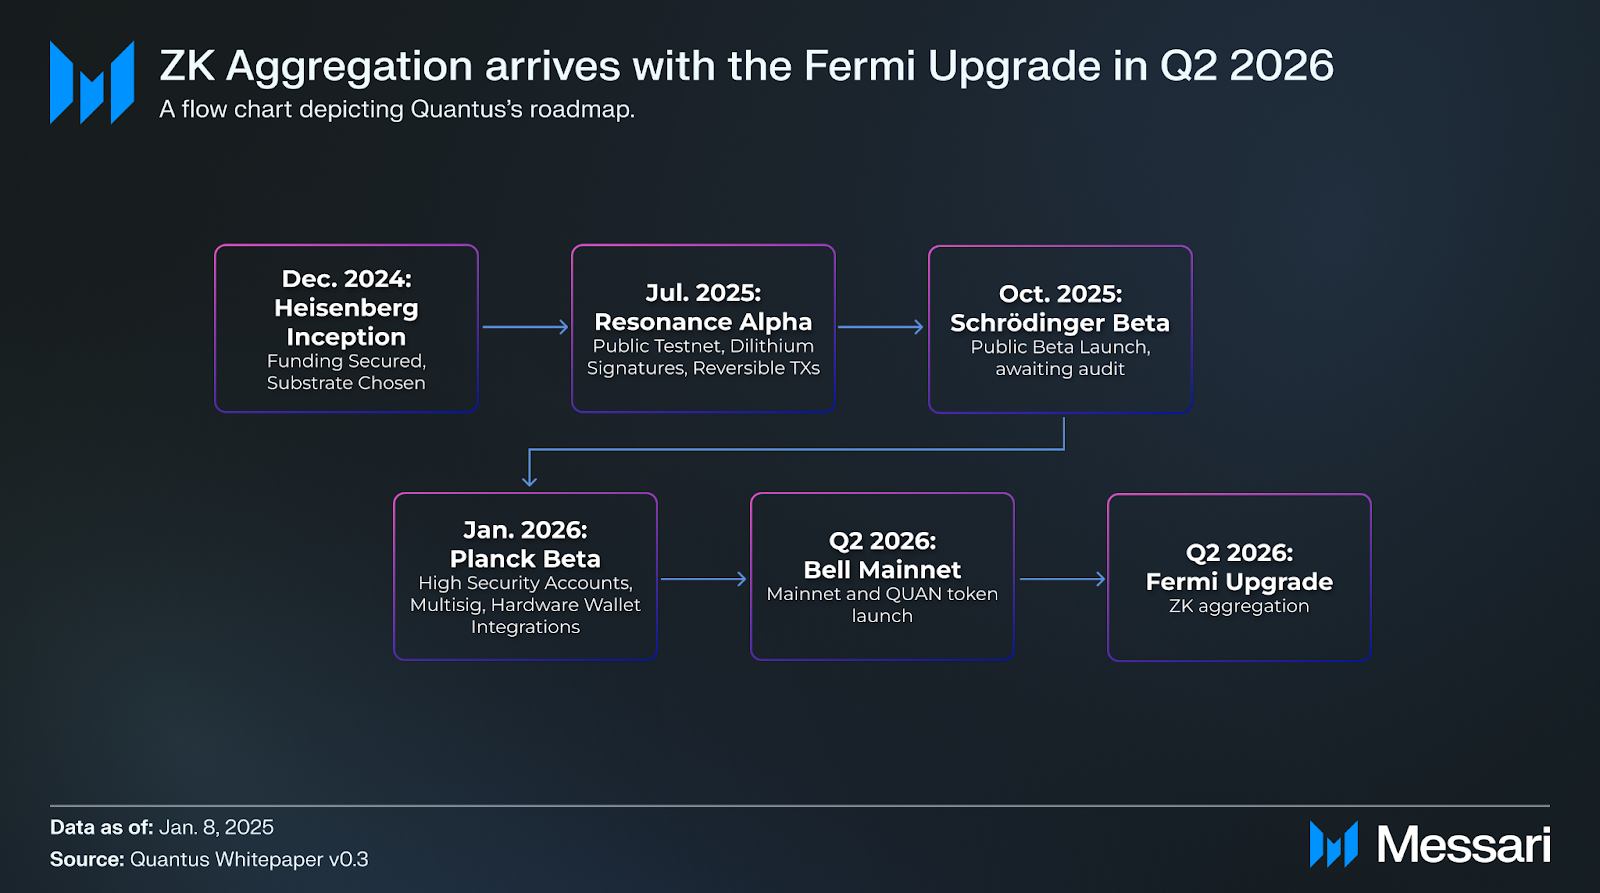
Quantus plans to launch its QUAN token and mainnet by the end of Q2 2026.
Introduction
Quantus Network was founded in 2024 by Christopher Smith and Joseph Mattia and is one of the first Layer-1 (L1) protocols attempting to protect digital assets from the quantum threat. Instead of waiting for legacy chains to adapt, Quantus has positioned itself as a wealth preservation blockchain with post-quantum cryptography and security features to defend users from a cryptographically relevant quantum computer (CRQC).
The Proof-of-Work (PoW) chain utilizes zero-knowledge proofs (ZKPs) and is built on Parity Technology'sSubstrate Software Development Kit (SDK). Substrate’s modularity allows for easy component replacement, provides flexibility (forkless runtime upgrades), and features a modern governance system (Substrate OpenGov) for onchain decision-making.
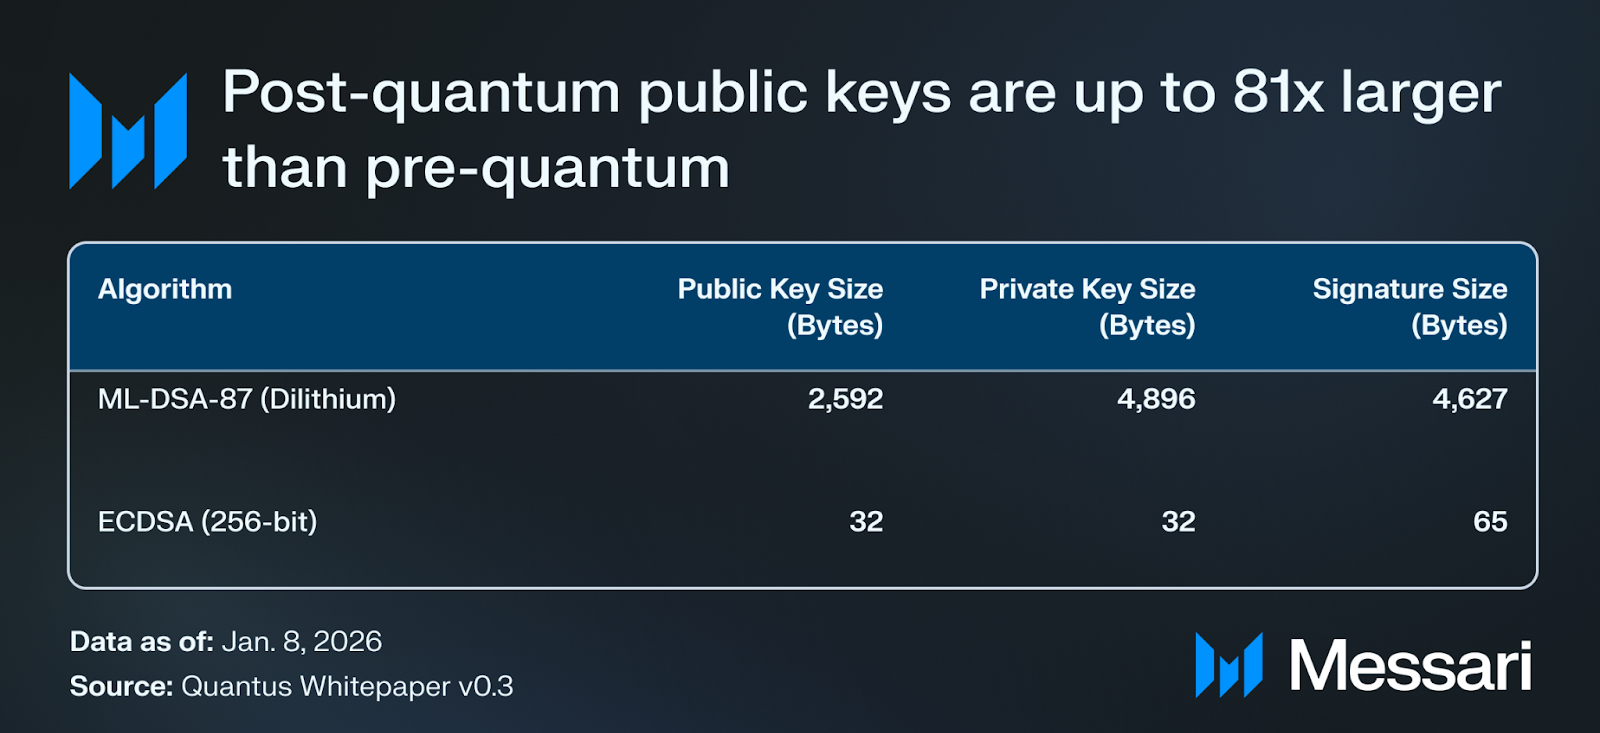
Quantus replaces SHA-256 with Poseidon2, a high-performance, algebraic hash function, to make the chain’s core computations more compatible with ZKP systems. Post-quantum signatures utilizing ML-DSA-87Dilithium are up to 80 times larger than their pre-quantum, ECDSA equivalents. This results in significantly more data per signature, leading to worse transactions per second (TPS) for the chain. As Q-day approaches, all blockchains with quantum-vulnerable signature schemes will need to adopt a quantum-secure standard. This sort of upgrade would leave Bitcoin, for example, with sub-1 TPS with current block sizes. Quantus’s architecture addresses scalability by introducing “Wormhole Addresses.” These addresses will leverage Plonky2, a high-performance, recursive STARK, in combination with Fast Reed-Solomon Interactive Oracle Proofs (FRI) to allow for computational heavy-lifting to take place offchain while being verifiable onchain thanks to ZKPs that can be generated with ease on modern CPUs.
The majority of today’s blockchains use public-key cryptography, which employs a pair of mathematically linked keys, public and private, for signatures. These mathematical links are rooted in trapdoor functions, or asymmetric mathematical problems computationally easy in one direction but practically impossible for classical computers in the other. The overwhelming majority of today’s blockchains, most notably Bitcoin and Ethereum, rely on elliptic-curve cryptography (ECC) for key pairs. This algorithm renders classical computers pragmatically ineffective in brute-force attacks. The number of operations required to derive a private key from a known public key is 2^128. This would take over 2.15 sextillion (2,150,000,000,000,000,000) years with a typical 5 GigaHertz (GHz) CPU, with improvements only providing linear speedups. However, quantum computers don’t follow the same rules. A classical computer bit exists in discrete states of 0 or 1. Quantum bits, or qubits, are able to exist in states of 0, 1, or both thanks to quantum superposition. Another significant property specific to quantum mechanics is quantum entanglement, where quantum particles (qubits in the context of quantum computing) become linked, allowing them to share a state. These characteristics enable quantum computers to explore many possibilities simultaneously, leading to massive speedups for specific complex problems such as optimization and cryptography.
This renders the security of nearly $3.0 trillion in digital assets vulnerable to CRQCs running quantum algorithms, such as Shor’s algorithm. This algorithm assumes a fault-tolerant, quantum computer and runs in polynomial time, whereas classical algorithms that crack ECC run in exponential time. A sufficiently powerful quantum computer running Shor’s algorithm can derive a private key from a known public key in a matter of hours. Assumptions on when this computer will exist vary, but the fact remains that it is an inevitability.
Why is Quantus Quantum-Secure?
Quantus leverages NIST-approved post-quantum algorithms to ensure that transaction signatures and peer-to-peer activity remain quantum-secure. Transactions are authorized using the Dilithium digital signature scheme, also known as ML-DSA. Dilithium is one of the NIST-selected post-quantum signature algorithms, based on hard lattice problems. Its signatures are significantly larger (4.6+ KB) than those using Elliptic Curve Digital Signature Algorithms (ECDSA, ~0.05 KB), but Quantus accepts this cost in exchange for long-term security. Network communications between nodes on Quantus use a post-quantum key exchange, also based on lattice problems, specifically Module Lattice Key Encapsulation Mechanisms (ML-KEM). This ensures that not only transaction signatures, but also peer-to-peer messages are protected against a quantum-equipped cyberattacker.
By using NIST-approved post-quantum algorithms, Quantus relies on well-vetted academic research. The team highlights that every layer, from the application down to networking, is quantum-safe.
ZK Scalability in Quantus
Quantus had to carefully develop its architecture to navigate post-quantum signature schemes as they are significantly larger than traditional ECDSA schemes. If each validator had to verify and store them for every transaction, throughput would degrade sharply. Quantus’s answer is to upgrade to ZKP aggregation in Q2 2026 with their Fermi upgrade. This pushes most of the computation offchain while letting the network verify a small, compact proof attesting to the validity of a large batch of activity, rather than re-checking each operation individually. These proofs can be generated in as little as 170 milliseconds and are ~100KB. This approach keeps node workload closer to “verify one proof” than “verify thousands of signatures,” allowing Quantus to efficiently scale.
Plonky2’s recursive SNARK technology makes these compact proofs possible, while Poseidon2 keeps blocks lightweight. Plonky2 is the chosen proving system because it is optimized for recursion, allowing it to efficiently combine multiple proofs into a single one. Poseidon2 is the hash function Quantus settled on because it is far more ZK-friendly than legacy hashes like SHA-256. SHA-256 inside ZK circuits is expensive due to its extensive use of bitwise operations. Translating these bitwise operations into arithmetic operations for the sake of the ZK circuit is computationally expensive. Poseidon2, on the other hand, is based on algebra; more suitable for ZK circuits. Together, Poseidon2 reduces the cost of proving the work, and Plonky2 makes it efficient to roll up multiple proofs into a single, verifiable package.
For example, a block might include a succinct proof representing thousands of transactions. This significantly reduces node workload and improves throughput, a crucial consideration given that post-quantum signatures and keys are bulkier. Quantus’s design goal is to achieve security and scalability concurrently, anticipating that future blockchains will experience a throughput bottleneck when they transition to post-quantum.
Quantus Wallet
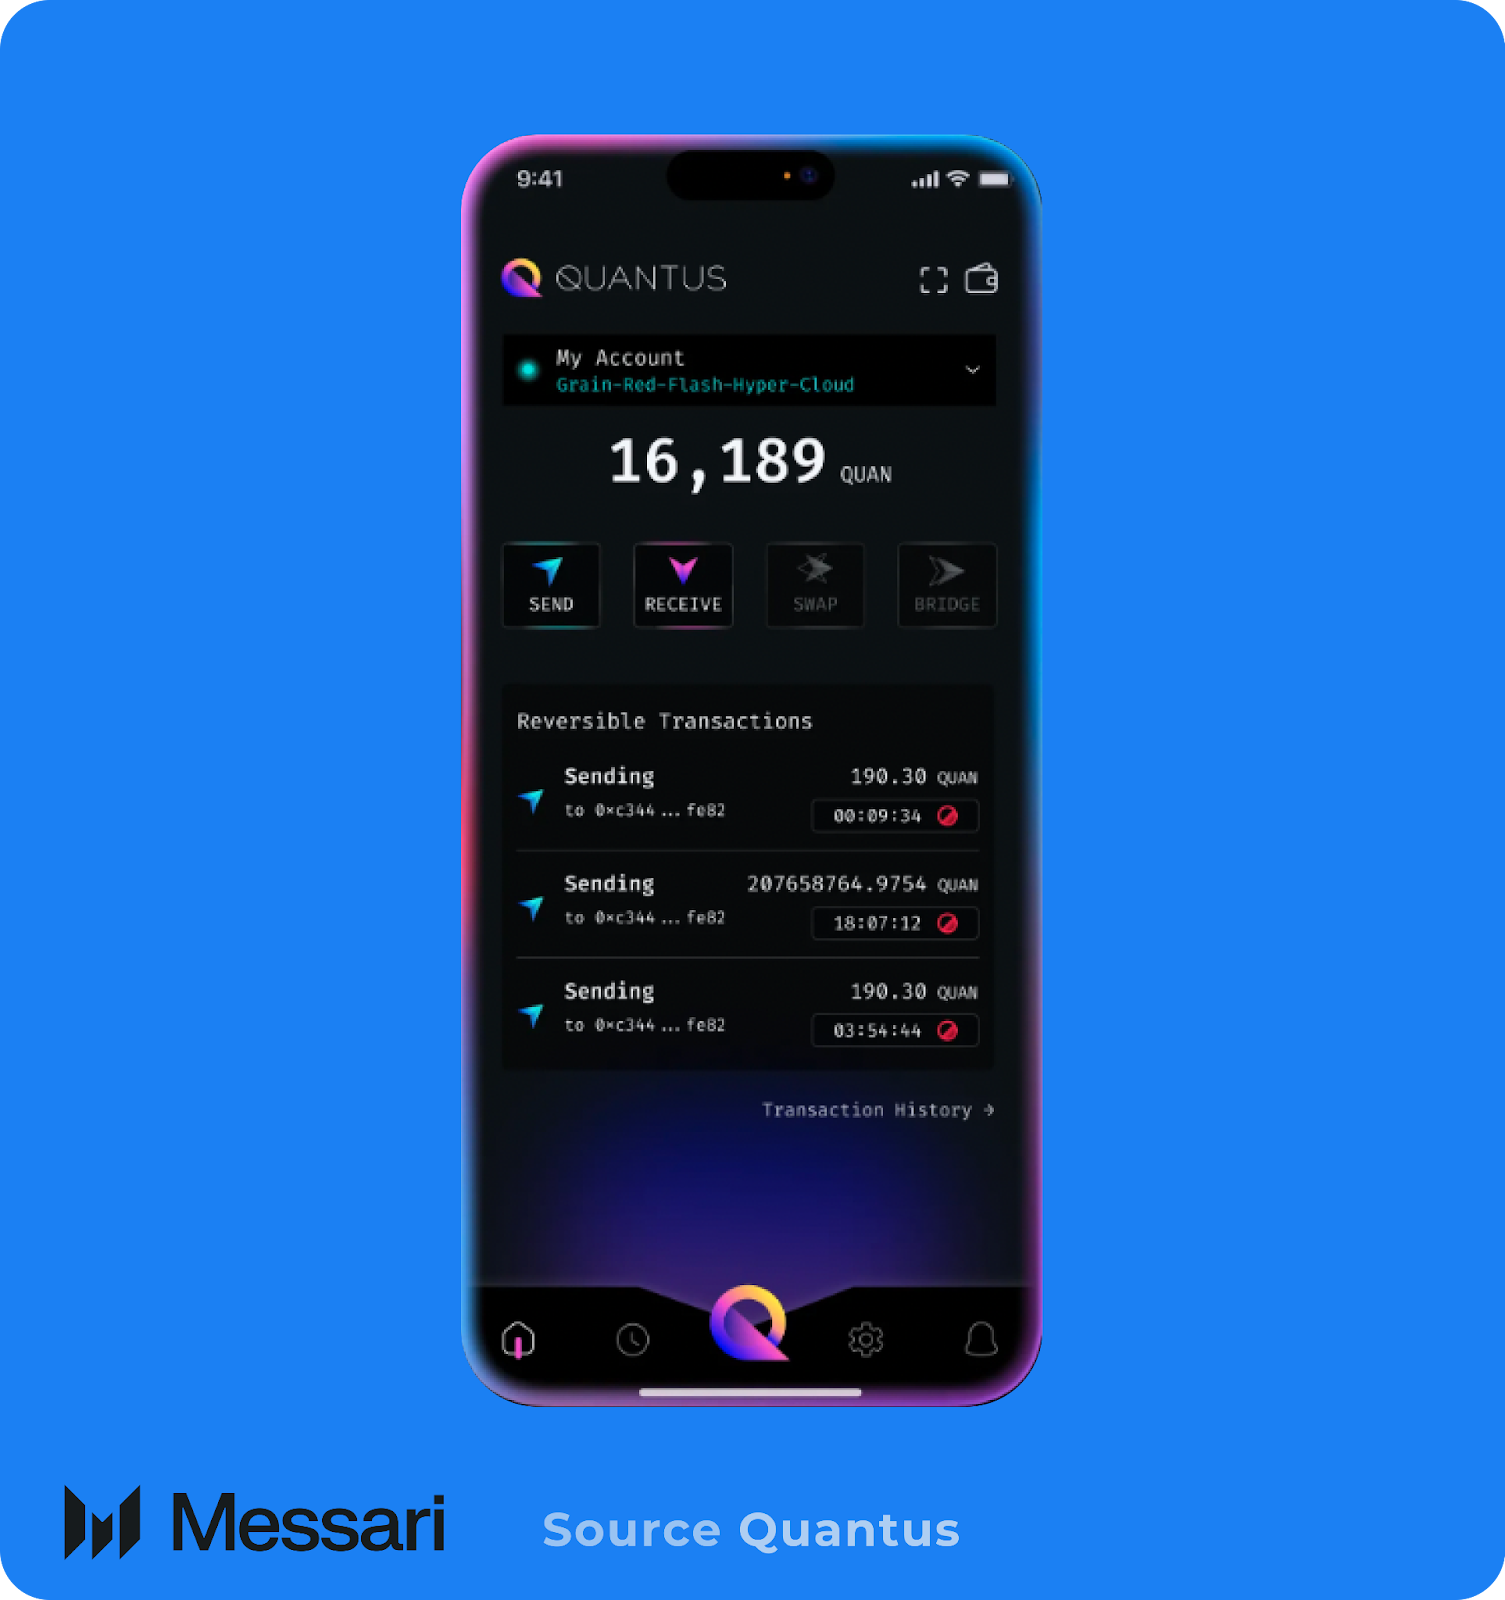
The Quantus Mobile App is available for iOS and Android devices. Quantus’s user-friendly wallet app aims to protect assets against quantum threats while maintaining a smooth and simple user experience. Quantus achieves this with the following features:
Reversible transactions: Reversible transactions introduce a delayed finality window after a transaction is submitted but before it becomes irreversible onchain. Users configure the reversible time period on their transactions, enabling them to cancel within the specified timeframe.
High-Security Account: Users can permanently enhance their security by opting for a High-Security Account, which establishes a standard reversal period for all outgoing transactions from the delegated wallet address. When enabling High-Security Accounts, the user sets the delay and a dedicated guardian/interceptor (e.g., a hardware wallet, multisig, or trusted third party) that has exclusive authority to cancel suspicious transactions during that window. If the guardian cancels, the funds are redirected to the guardian (not “rolled back” to the sender/receiver). As High-Security Accounts are opt-in, but permanent, an attacker who compromises the spending key cannot simply disable the safety controls. Guardians can also be High-Security Accounts with their own guardians, allowing for daisy-chained security hierarchies where each layer has superior permissions.
Security Guardians: Users can designate trusted contacts who have the ability to intercept a transaction before it completes.
Human-Friendly Addresses: Instead of long, cryptographic strings, the app uses readable checkphrases that are easier to recognize and reduce the risk of sending to the wrong address.
Beneficiary and Recovery Options: The app allows users to assign a recovery account or beneficiary, enabling assets to be transferred if they are unable to access their account.
Amongst all of these features, reversible transactions stand out as a wealth preservation opportunity for digital assets. By introducing cryptographically enforced, time-bound reversibility at the protocol layer, Quantus preserves the core benefits of decentralization while adding a crucial safety feature. This would shift the onchain experience from a zero-forgiveness system to one that more closely matches real-world economic behavior, where errors, fraud, and compromise are inevitable and not punished in absolute terms.
A reversible transaction framework could have meaningfully mitigated events like the ~$1.5 billion Bybit hack earlier this year, where stolen funds were immediately finalized and dispersed across the ecosystem before any coordinated response was possible. With reversibility windows, programmable rollback conditions, and security guardians, suspicious transactions could be halted, contested, or unwound before losses crystallize. More broadly, this primitive unlocks safer self-custody, consumer-grade wallets, compliant institutional adoption, and entirely new financial products that assume recoverability by default.
Quantus Testnet
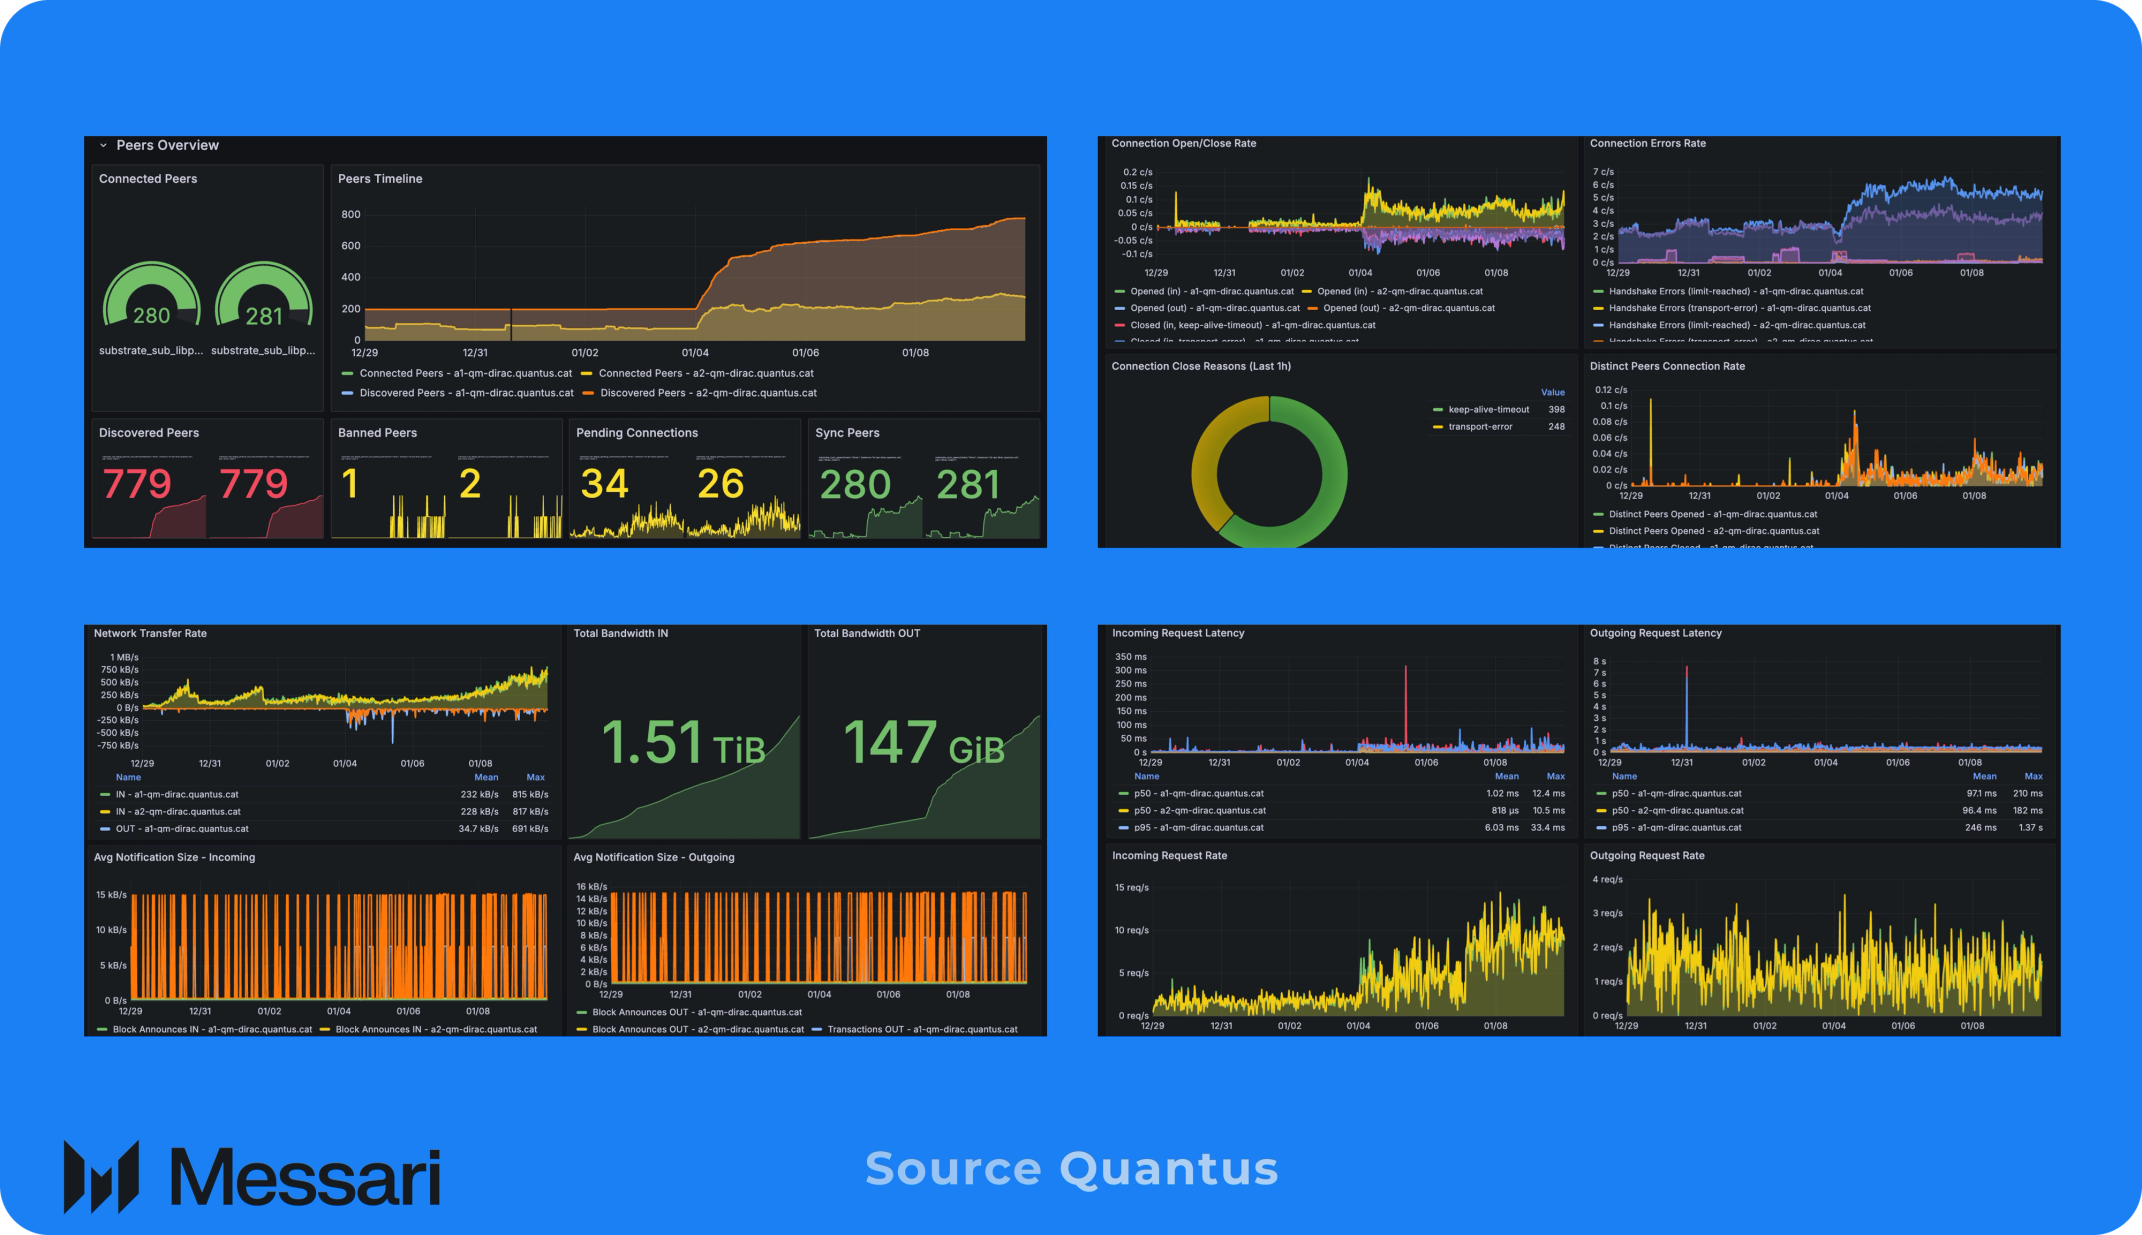
Quantus has tested its infrastructure with the previous Resonance alpha and Schrödinger beta. On Nov. 11, 2025, it rolled out its public testnet, Dirac, ahead of its mainnet release in Q1 2026 and the QUAN token generation event (TGE). Users can participate in the ecosystem by mining on the testnet or completing quests in the wallet. At the time of writing, the testnet has 231 users and an average block time of 13.64s. Users can test out features like security guardians and reversible transactions, and compete for rewards in the King of the Shill quest. Additionally, Quantus offers a comprehensive Grafana dashboard for those who wish to delve deeper into testnet performance.
Closing Summary
Quantus Network represents a forward-looking attempt to protect digital assets from Q-day by integrating post-quantum cryptography and innovative security features from the outset. Its development comes at a time when the broader industry is just beginning to grapple with quantum risks, post-quantum algorithms are being tested and chosen, and researchers are urging the adoption of long-term migration plans. Yet, many crypto developers and users might be erring on the side of complacency, given that functional quantum attacks still seem remote, but there are no fundamental breakthroughs left to achieve a CRQC. It is a matter of time now.
Quantus’s core thesis is that the cost of readiness is far lower than the cost of being caught unprepared. Even if strong quantum computers are 10 years or more away, infrastructure built now will leave the ecosystem in a much better position to respond when the time comes. That said, Quantus faces significant challenges and open questions. Its success will depend on adoption. Humans often need to learn the hard way, and convincing users to move onto a new chain for security reasons is hard, especially if that chain is young and not yet widely supported. The team is attempting to bootstrap usage by offering features that improve the overall user experience of self-custody. Quantus is marketing itself as both ultra-secure and user-friendly. If the platform can deliver competitive performance and potentially offer DeFi or DApp opportunities, it could establish its own community. The involvement of high-profile backers, such as Balaji Srinivasan, lends credibility and resources to the project, and its roadmap targets a mainnet launch by the end of Q1 2026.
This report was commissioned by Quantus Network. All content was produced independently by the author(s) and does not necessarily reflect the opinions of Messari, Inc. or the organization that requested the report. The commissioning organization may have input on the content of the report, but Messari maintains editorial control over the final report to retain data accuracy and objectivity. Author(s) may hold cryptocurrencies named in this report. This report is meant for informational purposes only. It is not meant to serve as investment advice. You should conduct your own research and consult an independent financial, tax, or legal advisor before making any investment decisions. Past performance of any asset is not indicative of future results. Please see our Terms of Service for more information.
No part of this report may be (a) copied, photocopied, duplicated in any form by any means or (b) redistributed without the prior written consent of Messari®.
Dillon is a Research Analyst on the Protocol Research team. He previously worked as an Automation/Mechatronics Engineer at Flex, Nike, and Target after graduating with a BSE in Mechanical Engineering from the University of Michigan - Ann Arbor. While he has maintained an interest in robotics, his interests lie in DeAI, privacy, prediction markets, and, more recently, quantum computing.
Dillon is a Research Analyst on the Protocol Research team. He previously worked as an Automation/Mechatronics Engineer at Flex, Nike, and Target after graduating with a BSE in Mechanical Engineering from the University of Michigan - Ann Arbor. While he has maintained an interest in robotics, his interests lie in DeAI, privacy, prediction markets, and, more recently, quantum computing.