AI is the primary demand driver for DeCC, as high‑value datasets like clinical trials, trading signals, medical records, and proprietary model weights cannot safely enter AI pipelines under centralized trust models.
Confidential data marketplaces and privacy-preserving AI workflows are becoming feasible with DeCC, enabling institutions to monetize or share insights from their data without surrendering raw access or regulatory compliance.
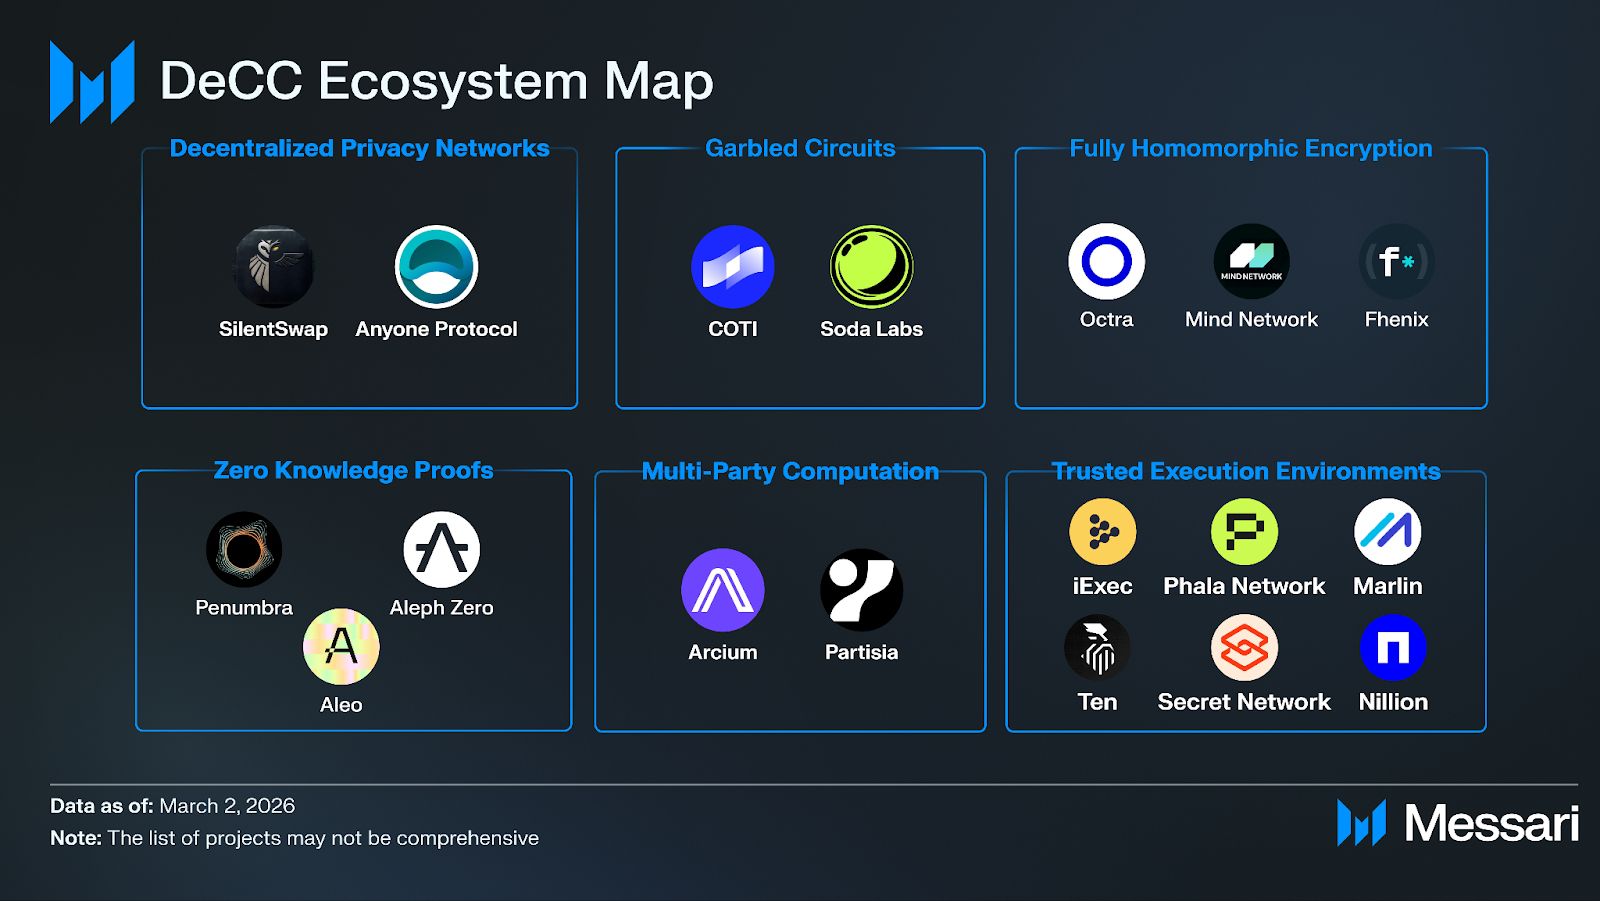
The DeCC ecosystem has matured into a multi-hundred-million-dollar category with an industry alliance, nearly 30 specialized projects, and adoption across financial services, privacy L1s/L2s, AI infrastructure, and enterprise-focused platforms.
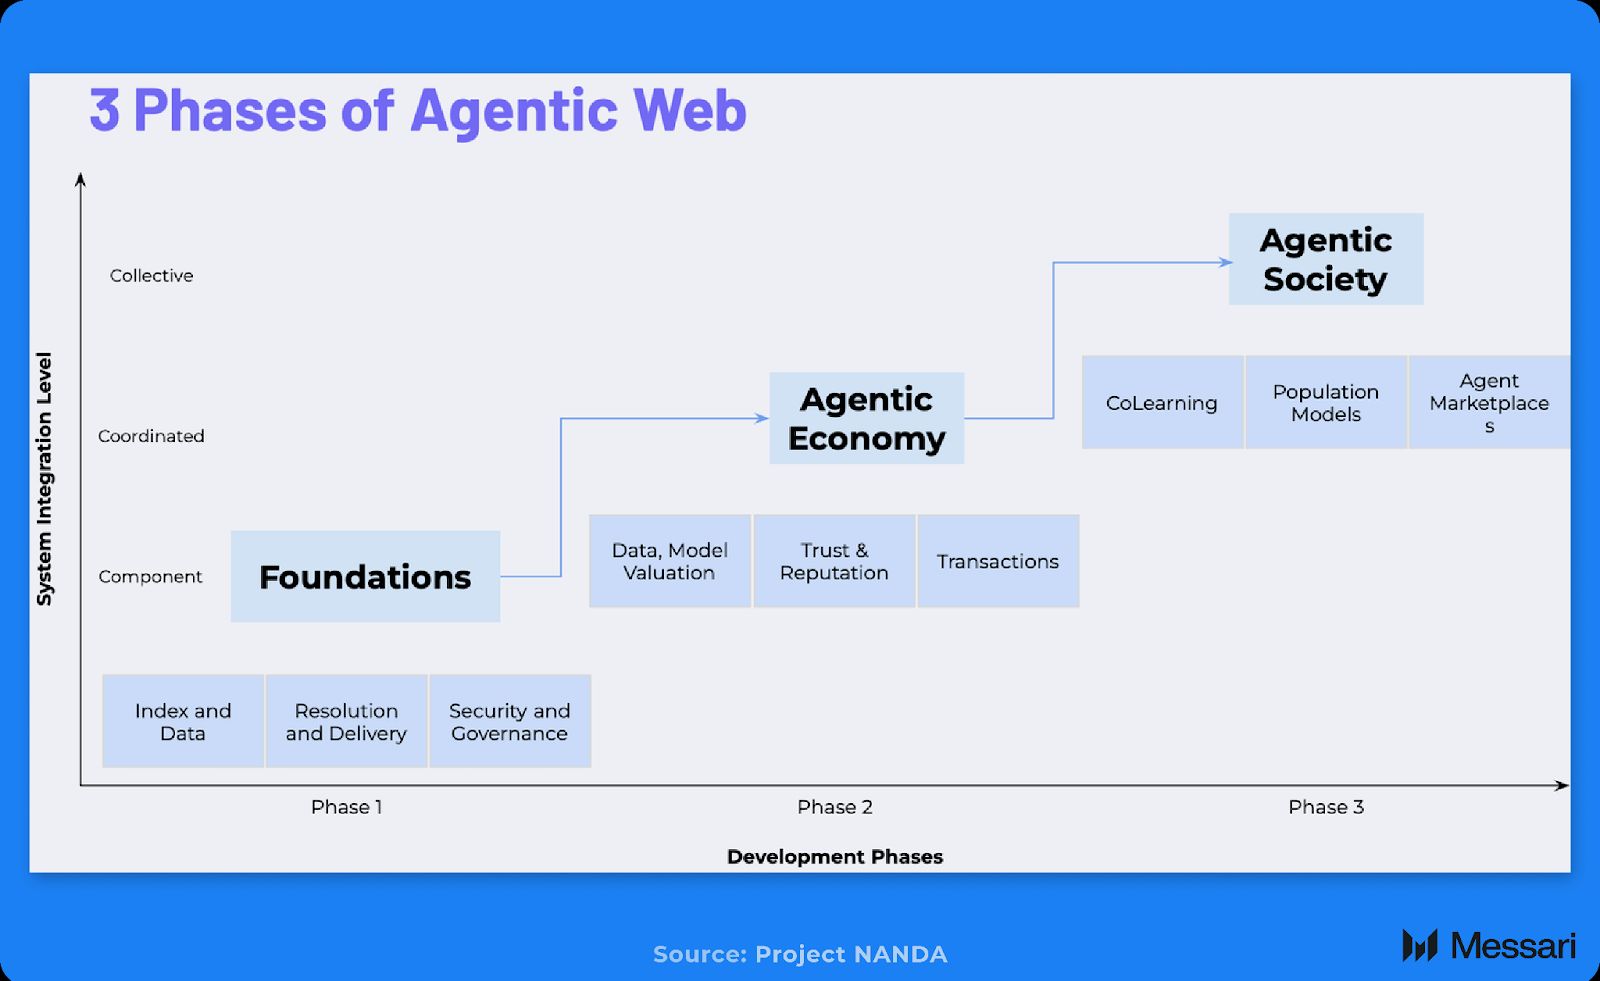
Emerging architectures like NANDA’s “Web3 Quilt” highlights DeCC as a foundational layer for an Internet of AI agents, where identities, reputations, and computations must span many registries and jurisdictions without leaking underlying data.
Primer
Standard encryption protects “data at rest” (stored on a disk) and in “transit” (moving across a network), but processing data still requires decrypting it first, exposing it in plaintext for the duration of computation. This is called the "data in use" gap. Decentralized Confidential Computing (DeCC) is a category of technology that enables blockchain applications to store and compute encrypted data without revealing it to the network or the public.
With traditional public blockchains, trustlessness is achieved through total transparency, as all smart contract states and transaction inputs are typically visible to everyone. DeCC addresses this limitation by providing a secure infrastructure that keeps sensitive data encrypted even during active processing, enabling decentralized applications to maintain a private state onchain.
DeCC eliminates the need to trust a single central operator or a transparent ledger with sensitive information and works by integrating several advanced cryptographic and hardware-based technologies to protect data throughout its entire lifecycle.
Key technical pillars include:
Trusted Execution Environments (TEEs): Hardware-based secure enclaves that isolate and process sensitive data separately from the rest of the system, protecting it even if the operating system is compromised.
Multi-Party Computation (MPC): A cryptographic technique that splits data into multiple encrypted shares distributed across different parties, allowing joint computation without revealing individual inputs.
Fully Homomorphic Encryption (FHE): An encryption method that enables computations to be performed directly on encrypted data, producing results that remain encrypted and can later be decrypted to reveal the correct output.
Zero-Knowledge Proofs (ZKPs): Cryptographic protocols that allow one party to prove the validity of a statement to another without disclosing any underlying data or secrets.
Garbled Circuits (GC): A cryptographic method that allows multiple parties to jointly compute a function over their private inputs without revealing them.
By combining these tools, DeCC ensures that at no point during the input, computation, or output phases does any unauthorized entity gain access to the raw, sensitive information.
AI as the Accelerant
AI has an unresolved data protection problem. Standard encryption secures data at rest and in transit, but AI models process it in plaintext for training, inference, and fine-tuning, potentially exposing sensitive inputs to the underlying infrastructure.
Currently, high-value datasets like clinical trials, proprietary trading signals, patient records, classified intelligence, and unreleased model weights remain inaccessible to AI due to strict access controls that prevent their use without exposure. Organizations must either centralize data in trusted cloud environments like AWS Nitro Enclaves or Azure Confidential Computing, accepting counterparty risk, or silo it and forgo the benefits of AI. The decision then becomes more intense when multiple parties need to collaborate. Three pharmaceutical firms cannot jointly train a drug-interaction model on combined patient data without one party, or a trusted third, seeing everything.
DeCC provides a third option by enabling computation over encrypted data. With FHE, a firm can contribute a dataset to a training pipeline without that pipeline ever seeing the data in plaintext. With MPC, multiple organizations can derive insights from pooled data without any single party accessing the others' inputs. With TEEs, AI inference can run in hardware enclaves where even the machine operator cannot observe the workload. These techniques allow proprietary data to generate value through AI without sacrificing confidentiality, making entire classes of datasets that were previously off-limits to model training and inference available for the first time.
With AI's rapid adoption across Web2 and Web3, solving this "data in use" vulnerability is becoming urgent. Centralized confidential compute still requires trusting a single operator not to be compromised, coerced by a government, or unilaterally change its terms of service. This centralized trust model limits how far high-value, multi-party datasets can safely go into AI pipelines, especially when adversaries, competitors, or cross-border institutions are involved. DeCC overcomes these constraints by distributing trust across independent participants and enforcing confidentiality and integrity with cryptography rather than contracts. By ensuring no single operator can access the data, observe workloads, or unilaterally interfere with computation, DeCC provides a more resilient foundation for AI that must operate on sensitive data at scale.
DeCC Use Cases
Data as an Asset
A financial institution’s loan book, distilled from decades of proprietary transaction history, is often a stronger predictor of credit risk than any public benchmark. A hospital’s imaging archive, built from years of clinical practice, can power diagnostic models that far outperform those trained on open medical datasets. The value of these assets depends on keeping them exclusive and under tight control.
DeCC lets institutions put this kind of confidential data to work without giving it away. Using techniques like FHE and MPC, a bank can contribute encrypted transaction histories to a shared fraud detection model, and a research hospital can include encrypted patient records in a multi-site clinical study. In both cases, the data is used in computation but never exposed in plaintext to other participants or the underlying infrastructure.
This unlocks the possibility of true confidential data marketplaces, where data owners monetize access to insights derived from their information while retaining full custody of the raw asset. In contrast to today’s digital economy, where selling data usually means permanently surrendering control, DeCC enables a model in which data can remain both protected and productively deployed.
Protecting Users and Consumers
The 2024 Change Healthcare data breach exposed medical records for tens of millions of Americans and was one of the largest healthcare data breaches in U.S. history. The breach was made possible because medical records were processed in plaintext on centralized infrastructure.
However, if medical records are processed using FHE or executed inside a TEE, the infrastructure handling them never holds a decryptable copy, thus there is nothing worth stealing. The same logic applies to all types of confidential data.
For blockchain applications specifically, DeCC closes a gap that has limited onchain adoption among mainstream users. Public blockchains are transparent and readable to anyone running a node, which is a feature for settlement finality and auditability, but is incompatible with privacy expectations for financial transactions, health data, and identity. DeCC enables onchain applications to inherit the trust guarantees of blockchain without requiring users to publish all of their sensitive data directly onchain.
Compliance
One of the least visible but most powerful brakes on data collaboration is regulatory fragmentation. Financial institutions, healthcare providers, and platforms must navigate overlapping regimes, such as GDPR in Europe, MiCA for digital assets, SEC oversight in the United States, and a growing web of local data sovereignty and sector-specific rules. These frameworks often pull in different directions, forcing organizations to choose between underusing their data or taking on legal and reputational risk.
DeCC offers a way to reconcile collaboration with compliance rather than forcing a tradeoff. Enabling computation over encrypted data allows institutions in different jurisdictions to participate in shared analytics or model training without ever disclosing raw records or moving plaintext data across borders. For example, a European bank and a U.S. bank can jointly build a fraud detection model using an MPC protocol in which each contributes encrypted transaction data. In this scenario, the resulting model is shared, but neither institution ever sees the other’s underlying data, and no plaintext crosses jurisdictions.
For regulators, this creates a new enforcement surface. They can require that certain checks, controls, or reporting computations be run in verifiable confidential environments, with cryptographic assurances that rules were followed, without demanding bulk data access. In this sense, compliance becomes a native use case for DeCC, turning privacy-preserving infrastructure into a tool that helps institutions satisfy regulatory obligations while unlocking cross-border, multi-party collaboration that would otherwise be impossible.
HSBC and Citibank use FHE for private asset tokenization, where transactions remain confidential while still fully auditable by regulators. Since 2020, ING has used zero-knowledge range proofs (ZKRPs) in mortgage processing, allowing the bank to verify borrower details while preserving the privacy of sensitive financial information.
Fhenix has emerged as a leading FHE infrastructure provider with applications spanning institutional finance and DeFi. Its CoFHE coprocessor went live on Base on February 5, 2026, offloading FHE operations from the main blockchain to improve efficiency without compromising decentralization. On December 30, 2025, Fhenix also introduced its Decomposable BFV scheme, which greatly reduces the cost of performing arithmetic on encrypted data, thus making DeCC more scalable. Its broader ecosystem includes confidential lending and private trading applications, with a focus on DeFi, confidential transactions, and privacy-preserving AI.
Zama, a confidential blockchain protocol that allows developers to build privacy-enabled smart contracts, already supports a wide ecosystem of financial applications, including banking apps like Raycash, stablecoin issuers like Tokenised GBP, and payments networks like Zaïffer.
Blockchains and Rollups
Aleo, a privacy-preserving Layer-1, compiles programs into ZK circuits executed by its SnarkVM. The ecosystem focuses on payments and supports stablecoins such as USDCx, a USDC-backed private stablecoin, and Paxos' USAD, a privacy stablecoin that shields user balances. On the identity side, Aleo supports zPass, an identity verification app that doesn’t leak personal data. zPass has already secured integrations with GeniiDAO for academic credential verification, Three of Cups for private identity verification, and Humine for medical research and clinical trial eligibility proofs.
Secret Network runs every smart contract inside Intel SGX enclaves, making it one of the original privacy-native chains. In November 2025, the network deployed a 2B-parameter "Solidity-LLM" inside SecretVM for private smart contract development and auditing. Secret's DeFi ecosystem includes the Shade Protocol suite and privacy-preserving NFTs via Stashh, with partnerships including Webisoft for dark pool trading and Fluid Tokens for collateralized lending. On the AI agent side, Secret has formed partnerships with Aethir, Eliza OS, Zekret, and Kuvi.ai for verifiable agent infrastructure. Total investment in the network stands at upwards of $400 million.
COTI, in partnership with Soda Labs, implements garbled circuits onchain as an Ethereum Layer-2 privacy overlay across over 70 networks. Penumbra operates as a Cosmos-based privacy zone for DeFi, supporting shielded swaps and MEV-resistant trading.
Identity, Compliance, and Selective Disclosure
One of DeCC's more practical capabilities is selective disclosure: proving a property about yourself without revealing the underlying data. A user can prove they are over 18 without disclosing their birthdate, or prove they are not on a sanctions list without revealing their identity.
Several of the projects covered above are building on this capability. Aleo's zPass (described in the Blockchains and Rollups section) handles credential verification for academic, medical, and identity use cases. Aztec's ZkPassport demonstrated compliance-grade sanctions screening during its token sale. Secret Network has pursued decentralized identity initiatives, including partnering with DataHaven to create an end-to-end privacy pipeline for storing, computing on, and validating sensitive data without public disclosure.
AI and Confidential Compute
Phala Network is a decentralized confidential computing platform that uses TEE-based infrastructure to enable privacy-preserving smart contract execution, AI inference, and offchain computation. Founded in 2019, Phala built one of the largest decentralized TEE networks before pivoting in 2025 toward full-stack confidential AI infrastructure and joining NVIDIA's Inception Program. On January 29, 2026, Phala shipped ERC-8004 agent deployment, a standard that extends agent-to-agent protocols with a Web3 trust layer, enabling onchain agent identity, discovery, and TEE-backed attestation.
Mind Network is an FHE-based trust and security layer for autonomous AI agent economies, backed by Binance Labs, Animoca Brands, and Chainlink, with two Ethereum Foundation grants for FHE research. Its "AgenticWorld" framework enables AI agents to transact and collaborate on encrypted data. In 2025, Mind Network became the first FHE project integrated byDeepSeek via its FHE Rust SDK, signed an MOU with BytePlus (ByteDance's cloud arm) to embed FHE-protected inference into enterprise platforms, partnered with Ant Digital on encrypted RWA messaging, and published its x402z Manifesto outlining HTTPZ, a zero-trust internet protocol for quantum-resistant, fully encrypted AI computation.
Nillion combines MPC, FHE, and TEEs into a unified "Blind Compute" stack through its Petnet network, enabling private AI inference via nilAI and encrypted storage via nilDB. After launching its alpha mainnet and TGE in March 2025, Nillion shipped its Phase 1 upgrade in Q4, introducing nilCC for general-purpose blind computation, and announced its migration to Ethereum.
iExec is a decentralized cloud platform that executes workloads inside TEEs. Its DataProtector toolkit enables confidential data monetization, while a 1 million RLC ecosystem fund supports builder adoption. In Q4 2025, iExec deployed its TEE privacy framework on Arbitrum and released Core v9.2.0 with bulk multi-dataset processing in TEE sessions, a feature designed to reduce AI training costs while preserving data privacy. The project is now advancing Intel TDX and GPU TEE support for confidential AI inference.
In Q1 2025, Secret Network launched SecretAI, a suite of open-source LLM models running inside confidential virtual machines powered by NVIDIA H100 and H200 GPUs paired with Intel TDX processors. Similar to Phala's confidential computing infrastructure for AI inference, SecretAI provides end-to-end privacy across inference, prompt history, training data, and computation, while also supporting encrypted agentic workloads. Later in November 2025, Secret shipped SecretVM, a general-purpose confidential VM framework that enables developers to deploy custom models, agents, and applications with hardware-backed privacy and cryptographic verifiability.
Octra is a general-purpose FHE network built on a proprietary hypergraph-based architecture, founded in 2021. The network functions as both a standalone Layer-1 and a decentralized, encrypted coprocessor for external ecosystems, including Ethereum and Solana. Octra raised $4 million in a pre-seed round led by Finality Capital Partners, with participation from Big Brain Holdings, Karatage, Presto Labs, and Builder Capital, followed by another $4 million through the angel investing platform Echo (acquired by Coinbase).
The network upgraded to mainnet alpha on Dec. 17, 2025, preserving full history since the genesis block, with the client supporting encrypt, transfer, decrypt, and deploy operations natively. A major upgrade planned for 2026 is expected to introduce full EVM compatibility, developer tools for programmable privacy, and integrations with Ethereum and Solana. 0xio, an ecosystem wallet and infrastructure provider, maintains a token list registry on the live network, and recent updates also indicate sustained OTC activity, with third parties accumulating OCT, Octra’s utility token used to pay for encrypted computations.
The most forward-looking challenge for DeCC lies in the emerging "Internet of AI Agents." The number of autonomous AI agents operating across enterprise and consumer applications is growing fast. As agent populations scale from thousands to potentially billions, they will need to discover, authenticate, and transact with each other across organizational boundaries. No existing system handles this.
MIT's Project NANDA, a Media Lab initiative building foundational infrastructure for an internet of AI agents, is constructing the index, protocols, and tools to address this. NANDA's architecture centers on a "Quilt of Registries," a federation layer that stitches many autonomous agent registries, both Web2 and Web3, into one globally discoverable fabric without creating a single point of control. The NANDA Index resolves agent handles to dynamic, cryptographically verifiable AgentFacts, providing discoverability and authentication at a scale that DNS-centered systems cannot support.
The Advanced AI Society (formerly Decentralized AI Society) has collaborated with Project NANDA on the "Web3 Quilt," the decentralized component of this agent infrastructure. The Web3 Quilt programming, presented at NANDA's MIT Summit in July 2025, included proposals for an "Index for Decentralized AI Agents" (I4DA) with technical discussions on verifying agent reputation, identity, and capabilities across heterogeneous, decentralized hubs.
Without decentralized reputation infrastructure, agents operating across different hubs can create aliases, fragment trust, and undermine accountability. If an agent's reputation is only valid within a single centralized platform, the agentic web becomes a patchwork of walled gardens. Hubs may be geographical (agents operating under EU versus U.S. regulatory regimes) or topic-based (DeFi agents versus healthcare agents), and reputations need to be portable across all of them.
DeCC technologies are the natural infrastructure layer here. MPC enables multiple registries to jointly verify agent credentials without exposing their internal data. ZKPs allow agents to prove attributes like compliance status or historical reliability without revealing sensitive operational details. TEEs provide hardware-enforced isolation for secure agent execution. This convergence is already being prototyped in NANDA's Phase 3 roadmap, which includes "Society of Agents" capabilities, including co-learning, agents operating across data silos with privacy guarantees, population AI, and privacy-preserving machine learning.
Closing Summary
DeCC began as a response to a narrow technical gap—how to compute on encrypted data without trusting a single operator—but it has quickly grown into a distinct ecosystem with real capital, standards, and production deployments. It now spans financial services, privacy layer-1s and layer-2s, FHE and MPC providers, and enterprise-focused networks.
Furthermore, the adoption of AI is turning this technology into an important part of onchain and online infrastructure. Models are running up against data that is valuable, regulated, or reputation-sensitive, and centralized confidential computing cannot fully solve the trust problem when multiple jurisdictions, competitors, or adversarial parties are involved. DeCC lets AI systems train and infer on that data without exposing it, anchoring trust in cryptography and decentralization instead of single operators or legal jurisdictions.
As DeCC becomes more widely adopted, it is likely that institutions like banks will use confidential compute for tokenization and compliance, privacy chains will make shielded assets and identity proofs routine, DeCC-native platforms will power private AI inference and agent economies, and enterprises will plug zero-trust compute into existing stacks. Over time, DeCC is likely to fade as a buzzword and become an assumption, underpinning blockchains with private state, data marketplaces where data never leaves the owner’s control, and AI agents that act across domains without leaking the data that powers them. In that world, decentralized confidential computing is not a feature but the base layer that keeps an AI-driven, globally connected economy usable and safe.
This report was commissioned by the DeCC Alliance. All content was produced independently by the author(s) and does not necessarily reflect the opinions of Messari, Inc. or the organization that requested the report. The commissioning organization may have input on the content of the report, but Messari maintains editorial control over the final report to retain data accuracy and objectivity. Author(s) may hold cryptocurrencies named in this report. This report is meant for informational purposes only. It is not meant to serve as investment advice. You should conduct your own research and consult an independent financial, tax, or legal advisor before making any investment decisions. Past performance of any asset is not indicative of future results. Please see our Terms of Service for more information.
No part of this report may be (a) copied, photocopied, duplicated in any form by any means or (b) redistributed without the prior written consent of Messari®.
Alexander is a protocol researcher specializing in Layer-1 and Layer-2 infrastructure, as well as RWA's and Stablecoins. Before Messari, he worked at Jump Trading and Bull-Moose Consulting. He graduated from Northeastern University with a degree in Economics and Data Science, and helped run Northeastern's blockchain club.
Alexander is a protocol researcher specializing in Layer-1 and Layer-2 infrastructure, as well as RWA's and Stablecoins. Before Messari, he worked at Jump Trading and Bull-Moose Consulting. He graduated from Northeastern University with a degree in Economics and Data Science, and helped run Northeastern's blockchain club.